Top Gear Romanian Hackers Deface The Telegraph

happygeek 1 Tallied Votes 296 Views Share

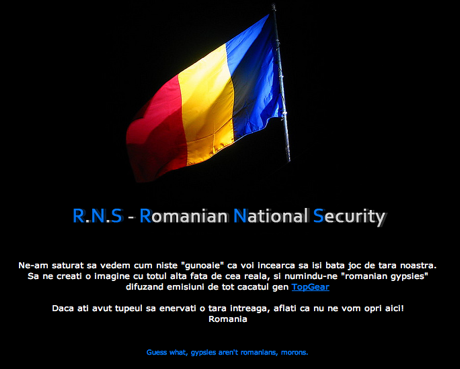
File under oops. The website of The Telegraph newspaper has been defaced by hackers, apparently upset at a cult British television show and the newspaper itself for mocking their country. The 'Romania National Security' hacking group has claimed responsibility for the attack which hit a couple of third party services advertising sub-domains used by The Telegraph. The very roughly translated statement posted by the group states that is "sick and tired of seeing how some "garbage" like you try to mock our country" and bemoans how TV shows such as Top Gear refer disparagingly about "Romanian Gypsies". Top Gear presenter James May also has a motoring column in The Sunday Telegraph.

Tony Osborn, a security expert at Symantec, warns that having your website defaced is "akin to business grinding to a halt" and that exposing how unwelcome visitors can re-write content without permission "hinders the business and affects its reputation". Osborn continues "The Daily Telegraph isn't the first website to have been defaced (nor will it be the last), we've seen many high profile sites affected with this problem. Also, it is worth noting that not all of the site was affected by the alleged Romanian hackers. However, it does come down to the issue of ensuring web fronting systems are secure to mitigate against the risk of those with malicious intent trying to harm the business and its reputation. Simple measures include applying basic information risk management, prioritising web facing systems and ensuring patches are always up to date. Also, if websites are outsourced, then the organisation must ensure the hosting provider has the necessary information governance practices and security measures in place".

Security exposé specialists Hackersblog has previously reported all databases at the Telegraph are vulnerable to a simple SQL injection attack , although at the time of writing it is not known if this was the attack vector used by the Romanian hackers.
Dani AI

Generated

This thread captures the news and a range of reactions from , , and , but it lacks a concise, practical incident-response checklist and clear long‑term hardening advice. Below are focused, actionable steps that complement the discussion without repeating the original reporting.

Immediate containment checklist:

  • Isolate the affected host/subdomain (remove from load balancer or set to a maintenance page).
  • Preserve evidence first: take disk/VM snapshots and copy web, app and database logs with timestamps.
  • If attacker appears active, snapshot then rotate credentials and revoke exposed API keys/sessions.
  • Notify the hosting provider and any third‑party vendor responsible for the affected subdomain.
  • Put a temporary WAF rule or IP blocks in place to stop obvious attack vectors while investigation proceeds.

Forensic and remediation priorities:

  • Inspect web and DB logs for unusual query strings, repeated POSTs, SQL keywords in parameters, and file‑modification timestamps.
  • Search the webroot for webshells, unexpected files or new admin accounts; export suspicious queries for later analysis.
  • Verify database user privileges and revoke unnecessary write/DDL rights from the web application account.
  • Fix root causes: remove vulnerable plugins, apply patches, and implement prepared statements/parameterized queries, e.g.:
using (var cmd = new SqlCommand("SELECT Id FROM Users WHERE username = @u", conn))
{
    cmd.Parameters.Add(new SqlParameter("@u", SqlDbType.NVarChar) { Value = username });
    using (var rdr = cmd.ExecuteReader()) { /* handle results */ }
}

Long‑term controls and legal cautions:

  • Enforce least privilege, regular integrity checks, automated backups with tested restores, periodic pen tests, and a WAF. Require SLAs and security attestations from any vendor managing subdomains. Praise for protest is understandable, but retaliation or hiring unknown "hackers" (as hinted by ) is illegal and risky; use certified security firms or coordinated disclosure instead. Defacement often signals deeper issues—treat it as a possible compromise and perform a full audit.
no,seriously 0 Newbie Poster

woooohooooooo serves them right

TudorBran 0 Newbie Poster

I totally agree with the Romanian hackers. I'm sick of people calling us "Romanian gypsies" or thieves only because we are from Romania. There are nice, hard-working people here as well, people that work 8 hours per day. At least now people will know that Romanians are smart and technology-aware.

hugoboss1 0 Newbie Poster

I want to meet a good hacker from romania, i got a deal for him/her...PM me at

Be a part of the DaniWeb community

We're a friendly, industry-focused community of developers, IT pros, digital marketers, and technology enthusiasts meeting, networking, learning, and sharing knowledge.