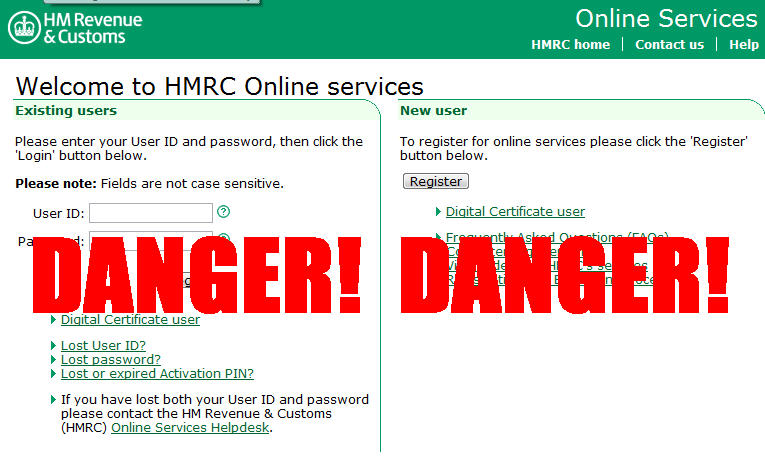
Stand up if you like paying your income tax. To all of you who have remained seated, which I will assume is indeed all of you, I have some more bad news: the bogus tax collectors want your money as well, and now they have botnets helping them.
According to a recent analysis by financial malware protection specialist Trusteer of just one botnet, specific to the UK market, it was actively looking for login information for users of the HM Revenue & Customs site where people can pay their income tax and VAT online. This botnet had details of more than 10,000 victims and included both full login credentials and passwords for the HMRC site. This is important, especially at this time of year, as in the UK there is a 31st July deadline for the self-employed to submit their second-instalments of income tax for the year. In a double whammy, those on low incomes also have to submit their tax credit claim renewals by the same date, and for many businesses it's also a filing date for quarterly VAT returns for good measure.
Connect the dots and the fact that botnets are actively targeting HMRC login data and the 31st July deadline is fast approaching is truly worrying. What it means is that there is likely to be an increase in the number of carefully targeted email phishing attacks on people whose login information has been compromised, as opposed to the usual 'spray and play' tactic adopted by the fake income tax return scammers at this time of year.
The danger now, says Trusteer, is that tax credit filers will click on unsolicited emails that look as though they might have been sent by HMRC, and in doing so, may end up infecting their home or office computers. "Back in February we warned online banking users of phishing and malware infections stemming from emails offering Internet users a tax refund. And given that such phishing emails are twice as successful as bank phishing attacks, cybercriminals have realised that an email with HMRC in its message header is a lot more attractive to recipients" said Mickey Boodaei, Trusteer's CEO.
The Trusteer CEO went on to say that tax credit and HMRC refunds dangle the `carrot' of free cash at Internet users, and persuades them to lower their normal credulity guard. Often the sites linked to by these fraudulent emails have what appear to be as the landing point. According to Boodaei, when Internet users receive what appears to be a tax credit or similar HMRC cash giveaway - or any deal that looks very tempting - the first thing they should do is move away from the computer and make a cup of tea, coffee or another favourite beverage. They should then sit down with their beverage, fire up a search engine and look for reports of a possible scam on the Net. For example, he says, entering the words 'HMRC tax refund email' into Google returns a series of links, the first one of which links directly to the official HMRC website and warns :
"HM Revenue & Customs (HMRC) would not inform customers of a tax rebate via email, or invite them to complete an online form to receive a rebate of tax. Do not visit the website contained within the email or disclose any personal or payment information."HM Revenue & Customs (HMRC) would not inform customers of a tax rebate via email, or invite them to complete an online form to receive a rebate of tax."