Hi there,

I am very very sick by having to fight this little bugger. I just cant get rid of this spam, spybot, trojan, hacktool, virus, whatever. I really need some professional help because if I can't fix this I will :cry: all day. I am going through some real life stuff right now and I seriously cant have this along with it. I need this system and just BLEAGH..

Go through this with me step by step and hopefully I can suddenly fix it.

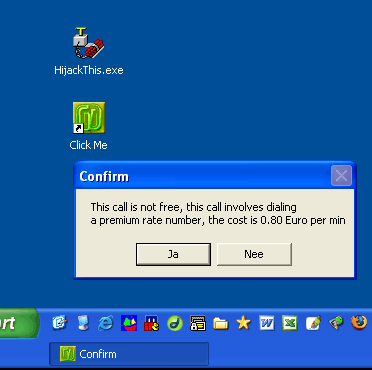
Ok, out of the blue I have this green little icon on my desktop that says Click me. Of course I know I didnt put it there, so I won't click it - but that is not even the point. Popup banners appear everywhere and various other virusses and trojans and worms start to appear as if they're having a party.

After fighting this all day I am now about to give up and throw away this damn computer (at least the hard drive)

PLEASE help me try to fight this, people always come to me to help them and I have nobody to turn to but hopefully you.

Today I have run at least 3 different anti spyware, bot destroyers, adware removers, anti virus and trojan hunters .. I've done safe mode reboots a zillion times to check and check again. And when everything says 0 found again I reboot and the f0kkuhr is there again.

Seriously, it is no longer funny for me anymore.

I never have issues, and if I do these programs catch them in time and remove them properly. But this one.. this little f0ckah I just cant get rid of.

What do you need to know? What is my FIRST step?

Attached is the screenshot of that damn green icon that keeps re-appearing on my desktop after each reboot, prompts me to yes/no for some dailup and during the time the system is on pops up at random some crap advertisements.

Do you recognize it? which worm, spyware, etc is this? Where do I find removal instructions on it?

Dani AI

Generated

Persistent, re‑appearing desktop items and random popups that come back after every reboot usually mean the infection is keeping a persistent component active (service, scheduled task/driver, shell extension or a hidden/rootkit layer). Treat the machine as compromised: isolate it from networks, stop using it for any sensitive logins, and prepare a clean rescue environment on a different, known‑clean PC before doing more work.

A practical triage sequence that goes beyond temp‑file cleanup:

  • Create a bootable rescue medium on a clean machine and scan the infected disk offline (this prevents reinfection while Windows is running).
  • Use dedicated tools to hunt persistence: an autorun/boot‑entry scanner to enumerate start‑up points, a process inspector to view parent/child relationships and digital signatures, and a rootkit detector for hidden modules. Run those tools from the rescue environment or from Safe Mode when needed so files can be removed without being re‑created.
  • Check scheduled tasks, services and system restore (restore points can reintroduce malware); clear or disable restore points before deleting active malicious files. When removing entries, delete the backing files offline whenever possible.

If the malware resists removal, preserve user data (documents, photos, mail stores) by copying only personal files to external media from the rescue environment, then perform a clean OS reinstall. After cleanup or reinstall: fully patch the OS, reinstall up‑to‑date AV, and change all online passwords from a known‑clean device; assume credentials used on the infected box were compromised.

As requested, sanitized logs help experts diagnose persistence; and as noted, temp cleanup is a good first step. For next help, supply updated autoruns output and a process snapshot (remove any personal paths or credentials first) so responders can point to the exact persistence mechanism to remove.

Recommended Answers

All 5 Replies

I see that you have a little HJT icon there too. Can you paste us your HJT log please? Thanks!

Logfile of HijackThis v1.99.1
Scan saved at 1:26:56, on 10-4-2005
Platform: Windows XP SP2 (WinNT 5.01.2600)
MSIE: Internet Explorer v6.00 SP2 (6.00.2900.2180)

Running processes:
C:\WINDOWS\System32\smss.exe
C:\WINDOWS\system32\winlogon.exe
C:\WINDOWS\system32\services.exe
C:\WINDOWS\system32\lsass.exe
C:\WINDOWS\System32\Ati2evxx.exe
C:\WINDOWS\system32\svchost.exe
C:\WINDOWS\System32\svchost.exe
C:\WINDOWS\system32\spoolsv.exe
C:\Program Files\Common Files\Symantec Shared\ccSetMgr.exe
C:\Program Files\Norton AntiVirus\navapsvc.exe
C:\Program Files\Norton AntiVirus\IWP\NPFMntor.exe
C:\Program Files\Common Files\Symantec Shared\SNDSrvc.exe
C:\Program Files\Common Files\Symantec Shared\SPBBC\SPBBCSvc.exe
C:\WINDOWS\System32\svchost.exe
C:\Program Files\Common Files\Symantec Shared\CCPD-LC\symlcsvc.exe
C:\Program Files\Common Files\Symantec Shared\ccEvtMgr.exe
C:\WINDOWS\system32\Ati2evxx.exe
C:\WINDOWS\Explorer.EXE
E:\Internet\DU Meter\DU Meter\DUMeter.exe
C:\PROGRA~1\Logitech\MOUSEW~1\SYSTEM\EM_EXEC.EXE
C:\Program Files\Motherboard Monitor 5\MBM5.EXE
C:\Program Files\Common Files\Symantec Shared\ccApp.exe
C:\WINDOWS\SOUNDMAN.EXE
E:\Adobe\acrobat\Distillr\Acrotray.exe
C:\Program Files\Pulse\Pulse.exe
E:\Internet\Trillian\trillian.exe
C:\PROGRAM FILES\INTERNET EXPLORER\IEXPLORE.EXE
C:\Program Files\Messenger\msmsgs.exe
C:\Documents and Settings\floris\Bureaublad\HijackThis.exe

R0 - HKCU\Software\Microsoft\Internet Explorer\Main,Start Page = http://www.vBulletin.nl/community/
R0 - HKLM\Software\Microsoft\Internet Explorer\Main,Start Page = http://www.vbulletin.nl/community
R0 - HKLM\Software\Microsoft\Internet Explorer\Search,SearchAssistant =
R0 - HKLM\Software\Microsoft\Internet Explorer\Search,CustomizeSearch =
R0 - HKLM\Software\Microsoft\Internet Explorer\Main,Local Page =
N3 - Netscape 7: user_pref("browser.startup.homepage", ""); (C:\Documents and Settings\floris\Application Data\Mozilla\Profiles\default\8bvnhz95.slt\)
N3 - Netscape 7: user_pref("browser.search.defaultengine", "http://www.google.com/"); (C:\Documents and Settings\floris\Application Data\Mozilla\Profiles\default\8bvnhz95.slt\)
O1 - Hosts: www.example.com
O4 - HKLM\..\Run: [DU Meter] E:\Internet\DU Meter\DU Meter\DUMeter.exe
O4 - HKLM\..\Run: [EM_EXEC] C:\PROGRA~1\Logitech\MOUSEW~1\SYSTEM\EM_EXEC.EXE
O4 - HKLM\..\Run: [MBM 5] "C:\Program Files\Motherboard Monitor 5\MBM5.EXE"
O4 - HKLM\..\Run: [Fortis Secure Layer Config] cseinst.exe -o-h
O4 - HKLM\..\Run: [SmcService] C:\PROGRA~1\Sygate\SPF\smc.exe -startgui
O4 - HKLM\..\Run: [ccApp] "C:\Program Files\Common Files\Symantec Shared\ccApp.exe"
O4 - HKLM\..\Run: [Symantec NetDriver Monitor] C:\PROGRA~1\SYMNET~1\SNDMon.exe
O4 - HKLM\..\Run: [SoundMan] SOUNDMAN.EXE
O4 - HKLM\..\Run: [Acrobat Assistant 7.0] "e:\Adobe\acrobat\Distillr\Acrotray.exe"
O4 - HKLM\..\Run: [firlnin] H:\TMP\Tijdelijke Internet-bestanden\Content.IE5\YHGRYLA5\delf061225[1].exe
O4 - HKLM\..\Run: [MCAgentExe] c:\PROGRA~1\mcafee.com\agent\mcagent.exe
O4 - HKLM\..\Run: [MCUpdateExe] C:\PROGRA~1\mcafee.com\agent\mcupdate.exe
O4 - HKLM\..\Run: [McRegWiz] C:\PROGRA~1\McAfee.com\Agent\McRegWiz.exe /autorun
O4 - HKLM\..\Run: [_AntiSpyware] C:\Program Files\McAfee\McAfee AntiSpyware\MssCli.exe
O4 - HKLM\..\Run: [etbrun] C:\windows\system32\elitecav32.exe
O4 - HKLM\..\Run: [ASDPLUGIN] C:\WINDOWS\system32\netherlands.exe -N
O4 - HKCU\..\Run: [Pulse] C:\Program Files\Pulse\Pulse.exe -splash
O4 - Global Startup: Adobe Gamma Loader.lnk = C:\Program Files\Common Files\Adobe\Calibration\Adobe Gamma Loader.exe
O6 - HKCU\Software\Policies\Microsoft\Internet Explorer\Control Panel present
O8 - Extra context menu item: Convert link target to Adobe PDF - res://e:\Adobe\acrobat\Acrobat\AcroIEFavClient.dll/AcroIECapture.html
O8 - Extra context menu item: Convert link target to existing PDF - res://e:\Adobe\acrobat\Acrobat\AcroIEFavClient.dll/AcroIEAppend.html
O8 - Extra context menu item: Convert selected links to Adobe PDF - res://e:\Adobe\acrobat\Acrobat\AcroIEFavClient.dll/AcroIECaptureSelLinks.html
O8 - Extra context menu item: Convert selected links to existing PDF - res://e:\Adobe\acrobat\Acrobat\AcroIEFavClient.dll/AcroIEAppendSelLinks.html
O8 - Extra context menu item: Convert selection to Adobe PDF - res://e:\Adobe\acrobat\Acrobat\AcroIEFavClient.dll/AcroIECapture.html
O8 - Extra context menu item: Convert selection to existing PDF - res://e:\Adobe\acrobat\Acrobat\AcroIEFavClient.dll/AcroIEAppend.html
O8 - Extra context menu item: Convert to Adobe PDF - res://e:\Adobe\acrobat\Acrobat\AcroIEFavClient.dll/AcroIECapture.html
O8 - Extra context menu item: Convert to existing PDF - res://e:\Adobe\acrobat\Acrobat\AcroIEFavClient.dll/AcroIEAppend.html
O8 - Extra context menu item: E&xport to Microsoft Excel - res://E:\Office\OFFICE11\EXCEL.EXE/3000
O16 - DPF: {2BC66F54-93A8-11D3-BEB6-00105AA9B6AE} (Symantec AntiVirus scanner) -
O16 - DPF: {6414512B-B978-451D-A0D8-FCFDF33E833C} (WUWebControl Class) -
O16 - DPF: {74D05D43-3236-11D4-BDCD-00C04F9A3B61} (HouseCall Besturing) - http://a840.g.
O16 - DPF: {C2FCEF52-ACE9-11D3-BEBD-00105AA9B6AE} (Symantec RuFSI Registry Information Class) -
O23 - Service: Adobe LM Service - Unknown owner - C:\Program Files\Common Files\Adobe Systems Shared\Service\Adobelmsvc.exe
O23 - Service: Ati HotKey Poller - ATI Technologies Inc. - C:\WINDOWS\System32\Ati2evxx.exe
O23 - Service: ATI Smart - Unknown owner - C:\WINDOWS\system32\ati2sgag.exe
O23 - Service: Symantec Event Manager (ccEvtMgr) - Symantec Corporation - C:\Program Files\Common Files\Symantec Shared\ccEvtMgr.exe
O23 - Service: Symantec Password Validation (ccPwdSvc) - Symantec Corporation - C:\Program Files\Common Files\Symantec Shared\ccPwdSvc.exe
O23 - Service: Symantec Settings Manager (ccSetMgr) - Symantec Corporation - C:\Program Files\Common Files\Symantec Shared\ccSetMgr.exe
O23 - Service: GEARSecurity - GEAR Software - C:\WINDOWS\System32\GEARSEC.EXE
O23 - Service: Macromedia Licensing Service - Macromedia - C:\Program Files\Common Files\Macromedia Shared\Service\Macromedia Licensing.exe
O23 - Service: McAfee AntiSpyware Real-Time Scanner (McAfeeAntiSpyware) - Network Associates, Inc. - C:\Program Files\McAfee\McAfee AntiSpyware\Msssrv.exe
O23 - Service: McAfee SecurityCenter Update Manager (mcupdmgr.exe) - Networks Associates Technology, Inc - C:\PROGRA~1\McAfee.com\Agent\mcupdmgr.exe
O23 - Service: Norton AntiVirus Auto-Protect Service (navapsvc) - Symantec Corporation - C:\Program Files\Norton AntiVirus\navapsvc.exe
O23 - Service: Norton AntiVirus Firewall Monitor Service (NPFMntor) - Symantec Corporation - C:\Program Files\Norton AntiVirus\IWP\NPFMntor.exe
O23 - Service: PestPatrol Remote - PestPatrol, Inc. - C:\Program Files\Common Files\PestPatrol\ppRemoteService.exe
O23 - Service: Sandra Data Service (SandraDataSrv) - SiSoftware - E:\SiSoftware Sandra Professional 2005\RpcDataSrv.exe
O23 - Service: Sandra Service (SandraTheSrv) - SiSoftware - E:\SiSoftware Sandra Professional 2005\RpcSandraSrv.exe
O23 - Service: SAVScan - Symantec Corporation - C:\Program Files\Norton AntiVirus\SAVScan.exe
O23 - Service: ScriptBlocking Service (SBService) - Symantec Corporation - C:\PROGRA~1\COMMON~1\SYMANT~1\SCRIPT~1\SBServ.exe
O23 - Service: Sygate Personal Firewall (SmcService) - Sygate Technologies, Inc. - C:\Program Files\Sygate\SPF\Smc.exe
O23 - Service: Symantec Network Drivers Service (SNDSrvc) - Symantec Corporation - C:\Program Files\Common Files\Symantec Shared\SNDSrvc.exe
O23 - Service: Symantec SPBBCSvc (SPBBCSvc) - Symantec Corporation - C:\Program Files\Common Files\Symantec Shared\SPBBC\SPBBCSvc.exe
O23 - Service: Symantec Core LC - Symantec Corporation - C:\Program Files\Common Files\Symantec Shared\CCPD-LC\symlcsvc.exe
O23 - Service: SymWMI Service (SymWSC) - Symantec Corporation - C:\Program Files\Common Files\Symantec Shared\Security Center\SymWSC.exe

But when I check a checkbox and click to fix it, it doesnt do dick. It appears to be ready, but when I click scan again it is still there.
No matter which item I select.

the confirm box is netherlands.exe

and after reboot and clearing out all procs from run, runonce, etc.. I get this:

Process list saved on 1:53:35, on 10-4-2005
Platform: Windows XP SP2 (WinNT 5.01.2600)
[pid] [full path to filename] [file version] [company name]
500 C:\WINDOWS\System32\smss.exe 5.1.2600.2180 Microsoft Corporation
584 C:\WINDOWS\system32\winlogon.exe 5.1.2600.2180 Microsoft Corporation
628 C:\WINDOWS\system32\services.exe 5.1.2600.2180 Microsoft Corporation
640 C:\WINDOWS\system32\lsass.exe 5.1.2600.2180 Microsoft Corporation
792 C:\WINDOWS\System32\Ati2evxx.exe 6.14.10.4112 ATI Technologies Inc.
808 C:\WINDOWS\system32\svchost.exe 5.1.2600.2180 Microsoft Corporation
940 C:\WINDOWS\System32\svchost.exe 5.1.2600.2180 Microsoft Corporation
1208 C:\WINDOWS\system32\spoolsv.exe 5.1.2600.2180 Microsoft Corporation
1468 C:\Program Files\Common Files\Symantec Shared\ccSetMgr.exe Symantec Corporation
1512 C:\WINDOWS\System32\GEARSEC.EXE GEAR Software
1552 C:\Program Files\McAfee\McAfee AntiSpyware\Msssrv.exe 1.0.1117.0 Network Associates, Inc.
1600 C:\Program Files\Norton AntiVirus\navapsvc.exe Symantec Corporation
1632 C:\Program Files\Norton AntiVirus\IWP\NPFMntor.exe Symantec Corporation
1672 C:\Program Files\Common Files\PestPatrol\ppRemoteService.exe PestPatrol, Inc.
1804 C:\Program Files\Common Files\Symantec Shared\SNDSrvc.exe Symantec Corporation
1852 C:\Program Files\Common Files\Symantec Shared\SPBBC\SPBBCSvc.exe Symantec Corporation
1880 C:\WINDOWS\System32\svchost.exe 5.1.2600.2180 Microsoft Corporation
1908 C:\Program Files\Common Files\Symantec Shared\CCPD-LC\symlcsvc.exe Symantec Corporation
180 C:\Program Files\Common Files\Symantec Shared\ccEvtMgr.exe Symantec Corporation
324 C:\Program Files\Common Files\pestpatrol\PPMCActiveDetection.exe PestPatrol, Inc.
1044 C:\WINDOWS\system32\Ati2evxx.exe 6.14.10.4112 ATI Technologies Inc.
1064 C:\WINDOWS\Explorer.EXE 6.0.2900.2180 Microsoft Corporation
2244 C:\WINDOWS\system32\wuauclt.exe 5.4.3790.2182 Microsoft Corporation
2484 E:\Internet\DU Meter\DU Meter\DUMeter.exe Hagel Technologies
2492 C:\Program Files\Motherboard Monitor 5\MBM5.EXE Alex van Kaam
2564 C:\Program Files\Pulse\Pulse.exe
3372 C:\Documents and Settings\floris\Bureaublad\HijackThis.exe Soeperman Enterprises Ltd.

DLLs loaded by process C:\WINDOWS\System32\smss.exe:
[full path to filename] [file version] [company name]
C:\WINDOWS\system32\ntdll.dll 5.1.2600.2180 Microsoft Corporation

This process will clean out your Temp files and your Temporary Internet Files. Please do both steps:

Step 1:Delete Temp Files
To clean out your temp files, click on Start and then run, and type %temp% and press the ok button.

This should open up the temp directory that your machine uses. Please delete all files that are found there. If you get an error when deleting a file, skip that file and delete all the others. If you had trouble deleting a file, reboot into Safe Mode and follow this step again. You should now be able to delete all the files.

Step 2: Delete Temporary Internet Files
Now I want you to open up Internet Explorer, and click on the Tools menu and then Internet Options. At the General tab, which should be the first tab you are currently on, click on the Delete Files button and put a checkmark in Delete offline content. Then press the OK button. This may take quite a while, so do not be alarmed with how long it takes. When it is done, your Temporary Internet Files will now be deleted.
,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,

Have Hijack This fix the following by placing a check in the appropriate boxes and selecting fix checked. Make sure all browser and all Windows Explorer windows are closed before fixing.
You might want to print out or copy & paste to notePad , these instructions as you will need to close this browser window to fix with hijackthis !

R0 - HKLM\Software\Microsoft\Internet Explorer\Search,SearchAssistant =

R0 - HKLM\Software\Microsoft\Internet Explorer\Search,CustomizeSearch =

R0 - HKLM\Software\Microsoft\Internet Explorer\Main,Local Page =

O1 - Hosts: www.example.com

O4 - HKLM\..\Run: [firlnin] H:\TMP\Tijdelijke Internet-bestanden\Content.IE5\YHGRYLA5\delf061225[1].exe


O4 - HKLM\..\Run: [etbrun] C:\windows\system32\elitecav32.exe

O4 - HKLM\..\Run: [ASDPLUGIN] C:\WINDOWS\system32\netherlands.exe -N

Fix this on unless you set it with spybot or something else .
O6 - HKCU\Software\Policies\Microsoft\Internet Explorer\Control Panel present.

Now reboot into safe mode and delete the following files and folders if found .

H:\TMP\Tijdelijke Internet-bestanden\Content.IE5\YHGRYLA5\delf061225[1].exe ,,,,,,,,delete file


C:\windows\system32\elitecav32.exe,,,,,,,delete file

C:\WINDOWS\system32\netherlands.exe,,,,,,,,,delete file

to delete the above files and folder you will need to do the following
go to
Show hidden files & folders

"Fix Checked"...Reboot to SAFE mode to delete files
How to start computer in safe mode

reboot computer and post a new log

Be a part of the DaniWeb community

We're a friendly, industry-focused community of developers, IT pros, digital marketers, and technology enthusiasts meeting, networking, learning, and sharing knowledge.