Hello guys,
I have problems with herss.exe for months. This spyware has extended not only to my computer but also to all of my usb keys and external disk. So whenever I scan and delete all of the files, it appears again after restart. Avast finds same stuff every day.
Even if everything looks ok on my computer, whenever I go with my usb key to some other computer, it gives virus alert (autorun.inf).
It is really frustrating, because I formatted the disk and installed fresh windows, but the spyware remains .
I also cannot view hidden files, I think it is connected with herss.exe.
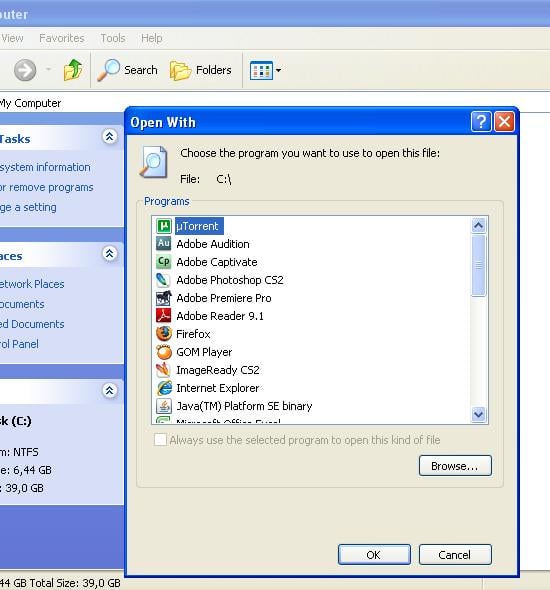
Whenever I try to open my local disk or any other disk in my computer, it asks me to choose the program for opening. I can only reach my disks with right click and explore option. I have attached image of this example.
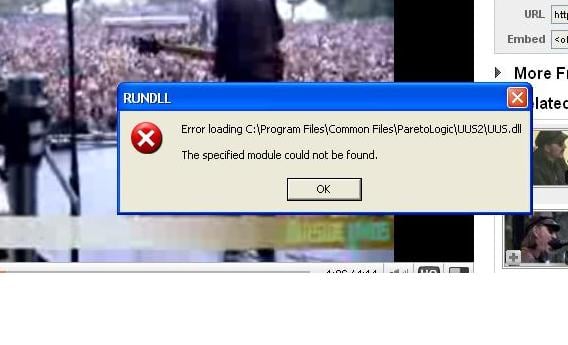
I also have windows errors every few hours. Picture of one example is also attached.
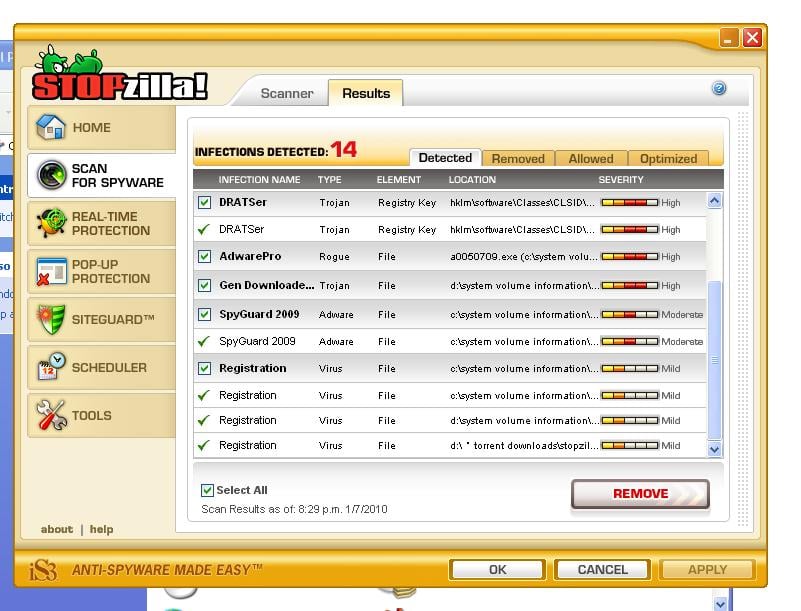
I have scanned my computer with stopzilla and I'm also attaching the picture of what was found.
Thank you for your help!
I hope we will find a solution!
Here are reports:
Malwarebytes' Anti-Malware 1.43
Database version: 3509
Windows 5.1.2600 Service Pack 2
Internet Explorer 7.0.5730.13
7.1.2010 22:43:36
mbam-log-2010-01-07 (22-43-36).txt
Scan type: Full Scan (C:\|D:\|F:\|G:\|H:\|I:\|)
Objects scanned: 204970
Time elapsed: 1 hour(s), 13 minute(s), 50 second(s)
Memory Processes Infected: 0
Memory Modules Infected: 0
Registry Keys Infected: 1
Registry Values Infected: 0
Registry Data Items Infected: 4
Folders Infected: 0
Files Infected: 5
Memory Processes Infected:
(No malicious items detected)
Memory Modules Infected:
(No malicious items detected)
Registry Keys Infected:
HKEY_CLASSES_ROOT\CLSID\MADOWN (Worm.Magania) -> Quarantined and deleted successfully.
Registry Values Infected:
(No malicious items detected)
Registry Data Items Infected:
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center\AntiVirusDisableNotify (Disabled.SecurityCenter) -> Bad: (1) Good: (0) -> Quarantined and deleted successfully.
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center\FirewallDisableNotify (Disabled.SecurityCenter) -> Bad: (1) Good: (0) -> Quarantined and deleted successfully.
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center\UpdatesDisableNotify (Disabled.SecurityCenter) -> Bad: (1) Good: (0) -> Quarantined and deleted successfully.
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Advanced\Folder\Hidden\SHOWALL\CheckedValue (Hijack.System.Hidden) -> Bad: (0) Good: (1) -> Quarantined and deleted successfully.
Folders Infected:
(No malicious items detected)
Files Infected:
C:\downloads\ostali programi\Cyberlink PowerCinema 5.0.3902\crack\cyberlink.powercinema.5.0.3902-NoPE.exe (Trojan.Downloader) -> Quarantined and deleted successfully.
C:\downloads\ostali programi\TechSmith SnagIt \keygen.exe (Malware.Tool) -> Quarantined and deleted successfully.
C:\Program Files\Cyberlink\PowerCinema\cyberlink.powercinema.5.0.3902-NoPE.exe (Trojan.Downloader) -> Quarantined and deleted successfully.
G:\System Volume Information\_restore{FB1C721E-1AD7-4422-BD15-D45EC036A5C0}\RP103\A0015502.exe (Trojan.Downloader) -> Quarantined and deleted successfully.
G:\System Volume Information\_restore{FB1C721E-1AD7-4422-BD15-D45EC036A5C0}\RP103\A0015534.exe (Malware.Packer) -> Quarantined and deleted successfully.
Avast
01/03/2010 20:53
Scan of all local drives
File C:\System Volume Information\_restore{7090D59B-C936-428B-A99B-AE248D072751}\RP156\A0048560.exe is infected by Win32:Malware-gen, Deleted
File C:\System Volume Information\_restore{7090D59B-C936-428B-A99B-AE248D072751}\RP156\A0048576.exe is infected by Win32:Malware-gen, Deleted
File C:\xmor.exe is infected by Win32:Malware-gen, Deleted
File D:\System Volume Information\_restore{7090D59B-C936-428B-A99B-AE248D072751}\RP156\A0048562.exe is infected by Win32:Malware-gen, Deleted
File D:\System Volume Information\_restore{7090D59B-C936-428B-A99B-AE248D072751}\RP156\A0048578.exe is infected by Win32:Malware-gen, Deleted
File D:\xmor.exe is infected by Win32:Malware-gen, Deleted
Number of searched folders: 6841
Number of tested files: 77962
Number of infected files: 6
----------------------------------------
01/07/2010 18:25
Scan of all local drives
File C:\anoataly.exe is infected by Win32:Trojan-gen, Deleted
File C:\Documents and Settings\Jure\Local Settings\Temp\cvasds1.dll is infected by Win32:Trojan-gen, Deleted
File C:\hiberfil.sys is infected by Win32:Rimecud-B [Wrm], Delete: Error 0xC0000043 {A file cannot be opened because the share access flags are incompatible.}, Delete: Error 0xC0000043 {A file cannot be opened because the share access flags are incompatible.}, Delete: Error 0xC0000043 {A file cannot be opened because the share access flags are incompatible.}, Delete: Error 0xC0000043 {A file cannot be opened because the share access flags are incompatible.}, Repair: Error 42060 {The file was not repaired.}
File C:\System Volume Information\_restore{7090D59B-C936-428B-A99B-AE248D072751}\RP163\A0050847.exe is infected by Win32:Trojan-gen, Deleted
File C:\System Volume Information\_restore{7090D59B-C936-428B-A99B-AE248D072751}\RP163\A0050861.exe is infected by Win32:Trojan-gen, Deleted
File C:\System Volume Information\_restore{7090D59B-C936-428B-A99B-AE248D072751}\RP163\A0050877.exe is infected by Win32:Trojan-gen, Deleted
File C:\System Volume Information\_restore{7090D59B-C936-428B-A99B-AE248D072751}\RP163\A0050888.exe is infected by Win32:Trojan-gen, Deleted
File C:\System Volume Information\_restore{7090D59B-C936-428B-A99B-AE248D072751}\RP164\A0050959.exe is infected by Win32:Trojan-gen, Deleted
File C:\System Volume Information\_restore{7090D59B-C936-428B-A99B-AE248D072751}\RP164\A0050986.exe is infected by Win32:Trojan-gen, Deleted
File C:\System Volume Information\_restore{7090D59B-C936-428B-A99B-AE248D072751}\RP166\A0051114.exe is infected by Win32:Trojan-gen, Deleted
File C:\System Volume Information\_restore{7090D59B-C936-428B-A99B-AE248D072751}\RP166\A0051134.exe is infected by Win32:Trojan-gen, Deleted
File C:\System Volume Information\_restore{7090D59B-C936-428B-A99B-AE248D072751}\RP167\A0051147.exe is infected by Win32:Trojan-gen, Deleted
File C:\System Volume Information\_restore{7090D59B-C936-428B-A99B-AE248D072751}\RP167\A0051160.exe is infected by Win32:Trojan-gen, Deleted
File D:\anoataly.exe is infected by Win32:Trojan-gen, Deleted
File D:\System Volume Information\_restore{7090D59B-C936-428B-A99B-AE248D072751}\RP163\A0050849.exe is infected by Win32:Trojan-gen, Deleted
File D:\System Volume Information\_restore{7090D59B-C936-428B-A99B-AE248D072751}\RP163\A0050863.exe is infected by Win32:Trojan-gen, Deleted
File D:\System Volume Information\_restore{7090D59B-C936-428B-A99B-AE248D072751}\RP163\A0050879.exe is infected by Win32:Trojan-gen, Deleted
File D:\System Volume Information\_restore{7090D59B-C936-428B-A99B-AE248D072751}\RP163\A0050890.exe is infected by Win32:Trojan-gen, Deleted
File D:\System Volume Information\_restore{7090D59B-C936-428B-A99B-AE248D072751}\RP163\A0050912.exe is infected by Win32:Rootkit-gen [Rtk], Deleted
File D:\System Volume Information\_restore{7090D59B-C936-428B-A99B-AE248D072751}\RP164\A0050946.exe is infected by Win32:Trojan-gen, Deleted
File D:\System Volume Information\_restore{7090D59B-C936-428B-A99B-AE248D072751}\RP164\A0050961.exe is infected by Win32:Trojan-gen, Deleted
File D:\System Volume Information\_restore{7090D59B-C936-428B-A99B-AE248D072751}\RP164\A0050988.exe is infected by Win32:Trojan-gen, Deleted
File D:\System Volume Information\_restore{7090D59B-C936-428B-A99B-AE248D072751}\RP165\A0051026.exe is infected by Win32:Trojan-gen, Deleted
File D:\System Volume Information\_restore{7090D59B-C936-428B-A99B-AE248D072751}\RP166\A0051080.exe is infected by Win32:Trojan-gen, Deleted
File D:\System Volume Information\_restore{7090D59B-C936-428B-A99B-AE248D072751}\RP166\A0051116.exe is infected by Win32:Trojan-gen, Deleted
File D:\System Volume Information\_restore{7090D59B-C936-428B-A99B-AE248D072751}\RP166\A0051136.exe is infected by Win32:Trojan-gen, Deleted
File D:\System Volume Information\_restore{7090D59B-C936-428B-A99B-AE248D072751}\RP167\A0051149.exe is infected by Win32:Trojan-gen, Deleted
File D:\System Volume Information\_restore{7090D59B-C936-428B-A99B-AE248D072751}\RP167\A0051161.exe is infected by Win32:Trojan-gen, Deleted
Number of searched folders: 6898
Number of tested files: 78929
Number of infected files: 28
DDS (Ver_09-12-01.01) - NTFSx86
Run by Jure at 0:05:29,28 on pet 08.01.2010
Internet Explorer: 7.0.5730.13 BrowserJavaVersion: 1.6.0_13
Microsoft Windows XP Professional 5.1.2600.2.1252.1.1033.18.1280.607 [GMT 1:00]
AV: AVG Anti-Virus *On-access scanning enabled* (Updated) {17DDD097-36FF-435F-9E1B-52D74245D6BF}
============== Running Processes ===============
C:\WINDOWS\system32\Ati2evxx.exe
C:\WINDOWS\system32\svchost -k DcomLaunch
C:\Program Files\Common Files\iS3\Anti-Spyware\SZServer.exe
svchost.exe
C:\WINDOWS\System32\svchost.exe -k netsvcs
svchost.exe
svchost.exe
C:\WINDOWS\system32\spoolsv.exe
C:\WINDOWS\system32\Ati2evxx.exe
C:\WINDOWS\Explorer.EXE
C:\WINDOWS\system32\ctfmon.exe
C:\Program Files\CyberLink\PowerCinema\Kernel\TV\CLCapSvc.exe
C:\Program Files\Diskeeper Corporation\Diskeeper\DkService.exe
C:\Program Files\Mozilla Firefox\firefox.exe
C:\Program Files\Java\jre6\bin\jqs.exe
C:\Program Files\Cyberlink\Shared files\RichVideo.exe
C:\Program Files\Analog Devices\SoundMAX\SMAgent.exe
C:\WINDOWS\system32\svchost.exe -k imgsvc
C:\Documents and Settings\Jure\Desktop\virus\orodja\dds.scr
============== Pseudo HJT Report ===============
uURLSearchHooks: H - No File
mURLSearchHooks: SrchHook Class: {d3f669eb-57ce-4f45-8fbd-e245cbb46366} - c:\program files\stopzilla!\toolbar\SZIESearchHook.dll
mURLSearchHooks: H - No File
BHO: ZILLAbar Browser Helper Object: {1827766b-9f49-4854-8034-f6ee26fcb1ec} - c:\program files\stopzilla!\toolbar\SZSG.dll
BHO: Adobe PDF Link Helper: {18df081c-e8ad-4283-a596-fa578c2ebdc3} - c:\program files\common files\adobe\acrobat\activex\AcroIEHelperShim.dll
BHO: {3CA2F312-6F6E-4B53-A66E-4E65E497C8C0} - No File
BHO: Java(tm) Plug-In 2 SSV Helper: {dbc80044-a445-435b-bc74-9c25c1c588a9} - c:\program files\java\jre6\bin\jp2ssv.dll
BHO: STOPzilla Browser Helper Object: {e3215f20-3212-11d6-9f8b-00d0b743919d} - c:\program files\stopzilla!\SZIEBHO.dll
BHO: JQSIEStartDetectorImpl Class: {e7e6f031-17ce-4c07-bc86-eabfe594f69c} - c:\program files\java\jre6\lib\deploy\jqs\ie\jqs_plugin.dll
TB: {CCC7A320-B3CA-4199-B1A6-9F516DD69829} - No File
TB: STOPzilla: {98828ded-a591-462f-83ba-d2f62a68b8b8} - c:\program files\stopzilla!\toolbar\SZSG.dll
uRun: [ctfmon.exe] c:\windows\system32\ctfmon.exe
IE: E&xport to Microsoft Excel - c:\progra~1\micros~2\office12\EXCEL.EXE/3000
IE: {e2e2dd38-d088-4134-82b7-f2ba38496583} - %windir%\Network Diagnostic\xpnetdiag.exe
IE: {92780B25-18CC-41C8-B9BE-3C9C571A8263} - {FF059E31-CC5A-4E2E-BF3B-96E929D65503} - c:\progra~1\micros~2\office11\REFIEBAR.DLL
DPF: {7530BFB8-7293-4D34-9923-61A11451AFC5} - hxxp://download.eset.com/special/eos/OnlineScanner.cab
DPF: {8AD9C840-044E-11D1-B3E9-00805F499D93} - hxxp://
DPF: {CAFEEFAC-0016-0000-0013-ABCDEFFEDCBA} - hxxp://
DPF: {CAFEEFAC-FFFF-FFFF-FFFF-ABCDEFFEDCBA} - hxxp://
TCP: {A476A0E0-0F31-44A4-997F-9ED6A2D2D142} = ,
Handler: skype4com - {FFC8B962-9B40-4DFF-9458-1830C7DD7F5D} - c:\progra~1\common~1\skype\SKYPE4~1.DLL
Notify: AtiExtEvent - Ati2evxx.dll
SSODL: WPDShServiceObj - {AAA288BA-9A4C-45B0-95D7-94D524869DB5} - c:\windows\system32\wpdshserviceobj.dll
================= FIREFOX ===================
FF - ProfilePath - c:\docume~1\jure\applic~1\mozilla\firefox\profiles\hgpf8lvz.default\
FF - component: c:\program files\stopzilla!\toolbar\extension\components\SiteGuardFF.dll
FF - HiddenExtension: Java Console: No Registry Reference - c:\program files\mozilla firefox\extensions\{CAFEEFAC-0016-0000-0013-ABCDEFFEDCBA}
---- FIREFOX POLICIES ----
c:\program files\mozilla firefox\greprefs\ - pref("security.ssl3.rsa_seed_sha", true);
============= SERVICES / DRIVERS ===============
R0 d347bus;d347bus;c:\windows\system32\drivers\d347bus.sys [2009-8-31 155136]
R0 d347prt;d347prt;c:\windows\system32\drivers\d347prt.sys [2009-8-31 5248]
R0 szkg5;szkg5;c:\windows\system32\drivers\SZKG.sys [2009-12-7 61328]
R0 szkgfs;szkgfs;c:\windows\system32\drivers\SZKGFS.sys [2009-12-14 163600]
R3 genmcmnUSB;USB Scroll Mouse Driver;c:\windows\system32\drivers\gflmouhid.sys [2003-8-7 6528]
R3 HomeQOS;HomeQOS Miniport;c:\windows\system32\drivers\homeqos.sys [2004-1-20 36096]
S0 is3srv;is3srv;c:\windows\system32\drivers\is3srv.sys [2009-12-7 61328]
S1 SBRE;SBRE;\??\c:\windows\system32\drivers\sbredrv.sys --> c:\windows\system32\drivers\SBREdrv.sys [?]
S3 Cdnsspcpc;Cdnsspcpc; [x]
=============== Created Last 30 ================
2010-01-07 22:26:24 240 ----a-w- c:\windows\system32\drivers\kgpcpy.cfg
2010-01-07 20:20:42 38224 ----a-w- c:\windows\system32\drivers\mbamswissarmy.sys
2010-01-07 20:20:39 19160 ----a-w- c:\windows\system32\drivers\mbam.sys
2010-01-07 20:20:39 0 d-----w- c:\program files\Malwarebytes' Anti-Malware
2010-01-06 12:55:31 439572484 ----a-w- C:\elektrokemija.mpg
2010-01-06 11:46:06 2939617280 ----a-w- C:\Video Composite_20100106_1246.mpg
2009-12-29 22:41:13 0 d-----w- c:\docume~1\jure\applic~1\STOPzilla!
2009-12-29 21:55:31 0 d-----w- c:\docume~1\alluse~1\applic~1\SITEguard
2009-12-29 21:53:48 0 d-----w- c:\program files\STOPzilla!
2009-12-29 21:53:47 0 d-----w- c:\program files\common files\iS3
2009-12-29 21:53:46 0 d-----w- c:\docume~1\alluse~1\applic~1\STOPzilla!
2009-12-29 21:48:55 0 d-----w- c:\program files\Trend Micro
2009-12-23 13:13:34 545424 ----a-r- c:\windows\system32\SZComp5.dll
2009-12-23 13:13:32 438928 ----a-r- c:\windows\system32\SZBase5.dll
2009-12-23 13:04:54 17408 ----a-r- c:\windows\system32\SZIO5.dll
2009-12-22 19:18:38 0 d-----w- c:\program files\MSXML 4.0
2009-12-22 19:17:55 0 d-----w- c:\program files\common files\Macrovision Shared
2009-12-21 18:57:23 51 --sh--r- C:\autorun.inf
2009-12-14 09:24:24 163600 ----a-r- c:\windows\system32\drivers\SZKGFS.sys
2009-12-10 15:11:40 126976 ----a-r- c:\windows\system32\IS3HTUI5.dll
2009-12-10 15:11:32 393216 ----a-r- c:\windows\system32\IS3DBA5.dll
2009-12-10 15:09:24 385024 ----a-r- c:\windows\system32\IS3UI5.dll
2009-12-10 15:09:08 61440 ----a-r- c:\windows\system32\IS3Hks5.dll
2009-12-10 15:08:48 23040 ----a-r- c:\windows\system32\IS3XDat5.dll
2009-12-10 15:06:52 225280 ----a-r- c:\windows\system32\IS3Win325.dll
2009-12-10 15:06:30 94208 ----a-r- c:\windows\system32\IS3Inet5.dll
2009-12-10 15:05:54 94208 ----a-r- c:\windows\system32\IS3Svc5.dll
2009-12-10 15:02:42 729088 ----a-r- c:\windows\system32\IS3Base5.dll
==================== Find3M ====================
2009-12-07 15:59:32 61328 ----a-r- c:\windows\system32\drivers\SZKG.sys
2009-12-07 15:59:32 61328 ----a-r- c:\windows\system32\drivers\is3srv.sys
2009-10-15 08:02:35 23296 ---ha-w- c:\windows\system32\mlfcache.dat
2009-06-01 13:28:10 32768 --sha-w- c:\windows\system32\config\systemprofile\local settings\history\history.ie5\mshist012009060120090602\index.dat
============= FINISH: 0:05:54,65 ===============
ESETSmartInstaller@High as CAB hook log:
OnlineScanner.ocx - registred OK
# version=7
# IEXPLORE.EXE=7.00.6000.20696 (vista_ldr.071008-1500)
# OnlineScanner.ocx=1.0.0.6211
# api_version=3.0.2
# EOSSerial=803cac2e9f616948987662a3e10205ab
# end=finished
# remove_checked=false
# archives_checked=false
# unwanted_checked=true
# unsafe_checked=false
# antistealth_checked=true
# utc_time=2010-01-07 11:01:36
# local_time=2010-01-08 12:01:36 (+0100, Central Europe Standard Time)
# country="Slovenia"
# lang=1033
# osver=5.1.2600 NT Service Pack 2
# compatibility_mode=258 16777214 0 2 777623 777623 0 0
# compatibility_mode=512 16777215 100 0 783701 783701 0 0
# compatibility_mode=768 16777215 100 0 358749 358749 0 0
# compatibility_mode=8192 67108863 100 0 3729 3729 0 0
# scanned=77299
# found=4
# cleaned=0
# scan_time=1860
C:\autorun.inf Win32/PSW.OnLineGames.NNU trojan 00000000000000000000000000000000 I
C:\downloads\ostali programi\Nero \Nero-_eng_full.exe Win32/Toolbar.AskSBar application 00000000000000000000000000000000 I
C:\Program Files\rmDC++0.403D[1]\rmDC.exe a variant of Win32/Packed.Morphine trojan 00000000000000000000000000000000 I
D:\autorun.inf Win32/PSW.OnLineGames.NNU trojan 00000000000000000000000000000000 I