This afternoon, I jumped out of my seat in surprise as avast! anti-virus sounded its siren, telling me that three of my connections on my browser were dangerous.
I closed all of my browser windows (I was running Chrome at the time), thinking nothing of it.
But now, whenever I perform a Google search, the search takes around fifteen seconds, and all of the links (excluding the cached ones) redirect my to "".
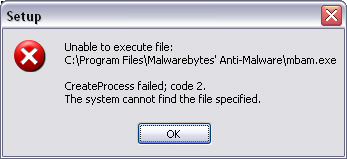
I've had a redirection problem before, and I was able to fix it pretty easily with some help from Malwarebytes' Anti-Malware. This, however is a different beast. When I install Malwarebytes' software, it immediately deletes the key executable. If I attempt to run the program straight from execution, the attached error pops up.
Anyways, here's my HiJackThis log:
Logfile of Trend Micro HijackThis v2.0.2
Scan saved at 5:29:53 PM, on 1/24/2010
Platform: Windows XP SP3 (WinNT 5.01.2600)
MSIE: Internet Explorer v7.00 (7.00.6000.16981)
Boot mode: Normal
Running processes:
C:\WINDOWS\System32\smss.exe
C:\WINDOWS\system32\winlogon.exe
C:\WINDOWS\system32\services.exe
C:\WINDOWS\system32\lsass.exe
C:\WINDOWS\system32\Ati2evxx.exe
C:\WINDOWS\system32\svchost.exe
C:\WINDOWS\System32\svchost.exe
C:\WINDOWS\system32\Ati2evxx.exe
C:\Program Files\Alwil Software\Avast4\aswUpdSv.exe
C:\Program Files\Alwil Software\Avast4\ashServ.exe
C:\WINDOWS\Explorer.EXE
C:\WINDOWS\RTHDCPL.EXE
C:\WINDOWS\SkyTel.EXE
C:\PROGRA~1\ALWILS~1\Avast4\ashDisp.exe
C:\Program Files\WebcamMax\CAMTHINS.exe
C:\Program Files\QuickTime\QTTask.exe
C:\Program Files\Microsoft Office\Office12\GrooveMonitor.exe
C:\Program Files\iTunes\iTunesHelper.exe
C:\Program Files\Java\jre6\bin\jusched.exe
C:\WINDOWS\system32\ctfmon.exe
C:\Program Files\DAEMON Tools Lite\daemon.exe
C:\WINDOWS\system32\spoolsv.exe
C:\Program Files\Common Files\Apple\Mobile Device Support\bin\AppleMobileDeviceService.exe
C:\Program Files\Bonjour\mDNSResponder.exe
C:\Program Files\Java\jre6\bin\jqs.exe
C:\WINDOWS\System32\svchost.exe
C:\Program Files\Alwil Software\Avast4\ashMaiSv.exe
C:\Program Files\Alwil Software\Avast4\ashWebSv.exe
C:\Program Files\iPod\bin\iPodService.exe
C:\Program Files\Adobe\Adobe Photoshop CS2\Photoshop.exe
C:\DOCUME~1\LUTHER~1\LOCALS~1\Temp\Adobelm_Cleanup.0001
C:\Program Files\Common Files\Adobe Systems Shared\Service\Adobelmsvc.exe
C:\DOCUME~1\LUTHER~1\LOCALS~1\Temp\Adobelm_Cleanup.0001
C:\Program Files\Mozilla Firefox\firefox.exe
C:\Documents and Settings\Luther Vespers\Desktop\Virus Killers\HiJackThis\HijackThis.exe
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Default_Page_URL =
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Default_Search_URL = http://go.microsoft.com/fwlink/?LinkId=54896
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Search Page = http://go.microsoft.com/fwlink/?LinkId=54896
R0 - HKLM\Software\Microsoft\Internet Explorer\Main,Start Page =
R1 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyOverride = *.local
N2 - Netscape 6: user_pref("browser.search.defaultengine", "http://www.google.com/"); (C:\Documents and Settings\LUTHER VESPERS\Application Data\Mozilla\Profiles\default\ztgzpvyj.slt\)
O2 - BHO: Adobe PDF Reader Link Helper - {06849E9F-C8D7-4D59-B87D-784B7D6BE0B3} - C:\Program Files\Common Files\Adobe\Acrobat\ActiveX\AcroIEHelper.dll
O2 - BHO: Groove GFS Browser Helper - {72853161-30C5-4D22-B7F9-0BBC1D38A37E} - C:\Program Files\Microsoft Office\Office12\GrooveShellExtensions.dll
O2 - BHO: (no name) - {7E853D72-626A-48EC-A868-BA8D5E23E045} - (no file)
O2 - BHO: (no name) - {d43e9604-c5c9-4b40-9292-9b9b24b508b5} - pihenedo.dll (file missing)
O2 - BHO: Java(tm) Plug-In 2 SSV Helper - {DBC80044-A445-435b-BC74-9C25C1C588A9} - C:\Program Files\Java\jre6\bin\jp2ssv.dll
O2 - BHO: JQSIEStartDetectorImpl - {E7E6F031-17CE-4C07-BC86-EABFE594F69C} - C:\Program Files\Java\jre6\lib\deploy\jqs\ie\jqs_plugin.dll
O4 - HKLM\..\Run: [RTHDCPL] RTHDCPL.EXE
O4 - HKLM\..\Run: [SkyTel] SkyTel.EXE
O4 - HKLM\..\Run: [avast!] C:\PROGRA~1\ALWILS~1\Avast4\ashDisp.exe
O4 - HKLM\..\Run: [Google Desktop Search] "C:\Program Files\Google\Google Desktop Search\GoogleDesktop.exe" /startup
O4 - HKLM\..\Run: [IMJPMIG8.1] "C:\WINDOWS\IME\imjp8_1\IMJPMIG.EXE" /Spoil /RemAdvDef /Migration32
O4 - HKLM\..\Run: [MSPY2002] C:\WINDOWS\system32\IME\PINTLGNT\ImScInst.exe /SYNC
O4 - HKLM\..\Run: [PHIME2002ASync] C:\WINDOWS\system32\IME\TINTLGNT\TINTSETP.EXE /SYNC
O4 - HKLM\..\Run: [PHIME2002A] C:\WINDOWS\system32\IME\TINTLGNT\TINTSETP.EXE /IMEName
O4 - HKLM\..\Run: [Adobe Reader Speed Launcher] "C:\Program Files\Adobe\Reader 8.0\Reader\Reader_sl.exe"
O4 - HKLM\..\Run: [WebcamMaxMoniter] "C:\Program Files\WebcamMax\CAMTHINS.exe" /m
O4 - HKLM\..\Run: [QuickTime Task] "C:\Program Files\QuickTime\QTTask.exe" -atboottime
O4 - HKLM\..\Run: [GrooveMonitor] "C:\Program Files\Microsoft Office\Office12\GrooveMonitor.exe"
O4 - HKLM\..\Run: [iTunesHelper] "C:\Program Files\iTunes\iTunesHelper.exe"
O4 - HKLM\..\Run: [AdobeCS4ServiceManager] "C:\Program Files\Common Files\Adobe\CS4ServiceManager\CS4ServiceManager.exe" -launchedbylogin
O4 - HKLM\..\Run: [SunJavaUpdateSched] "C:\Program Files\Java\jre6\bin\jusched.exe"
O4 - HKLM\..\Run: [luwahejeso] Rundll32.exe "hunupave.dll",s
O4 - HKLM\..\RunOnce: [Malwarebytes' Anti-Malware] C:\Program Files\Malwarebytes' Anti-Malware\mbamgui.exe /install /silent
O4 - HKCU\..\Run: [ctfmon.exe] C:\WINDOWS\system32\ctfmon.exe
O4 - HKCU\..\Run: [Google Update] "C:\Documents and Settings\Luther Vespers\Local Settings\Application Data\Google\Update\GoogleUpdate.exe" /c
O4 - HKCU\..\Run: [DAEMON Tools Lite] "C:\Program Files\DAEMON Tools Lite\daemon.exe" -autorun
O4 - Startup: Adobe Gamma.lnk = C:\Program Files\Common Files\Adobe\Calibration\Adobe Gamma Loader.exe
O4 - Startup: ImpulseNow.lnk = C:\Program Files\Stardock\Impulse\Now\ImpulseNow.exe
O4 - Startup: Stardock ObjectDock.lnk = C:\Program Files\Stardock\Object Desktop\ObjectDock\ObjectDock.exe
O8 - Extra context menu item: E&xport to Microsoft Excel - res://C:\PROGRA~1\MICROS~2\Office12\EXCEL.EXE/3000
O9 - Extra button: Send to OneNote - {2670000A-7350-4f3c-8081-5663EE0C6C49} - C:\PROGRA~1\MICROS~2\Office12\ONBttnIE.dll
O9 - Extra 'Tools' menuitem: S&end to OneNote - {2670000A-7350-4f3c-8081-5663EE0C6C49} - C:\PROGRA~1\MICROS~2\Office12\ONBttnIE.dll
O9 - Extra button: Bonjour - {7F9DB11C-E358-4ca6-A83D-ACC663939424} - C:\Program Files\Bonjour\ExplorerPlugin.dll
O9 - Extra button: Research - {92780B25-18CC-41C8-B9BE-3C9C571A8263} - C:\PROGRA~1\MICROS~2\Office12\REFIEBAR.DLL
O9 - Extra button: (no name) - {e2e2dd38-d088-4134-82b7-f2ba38496583} - C:\WINDOWS\Network Diagnostic\xpnetdiag.exe
O9 - Extra 'Tools' menuitem: @xpsp3res.dll,-20001 - {e2e2dd38-d088-4134-82b7-f2ba38496583} - C:\WINDOWS\Network Diagnostic\xpnetdiag.exe
O9 - Extra button: Messenger - {FB5F1910-F110-11d2-BB9E-00C04F795683} - C:\Program Files\Messenger\msmsgs.exe
O9 - Extra 'Tools' menuitem: Windows Messenger - {FB5F1910-F110-11d2-BB9E-00C04F795683} - C:\Program Files\Messenger\msmsgs.exe
O16 - DPF: {6E32070A-766D-4EE6-879C-DC1FA91D2FC3} (MUWebControl Class) -
O17 - HKLM\System\CCS\Services\Tcpip\..\{5BE80C94-55CB-470E-971C-D0F777F2950F}: NameServer = ,,
O18 - Protocol: grooveLocalGWS - {88FED34C-F0CA-4636-A375-3CB6248B04CD} - C:\Program Files\Microsoft Office\Office12\GrooveSystemServices.dll
O18 - Protocol: skype4com - {FFC8B962-9B40-4DFF-9458-1830C7DD7F5D} - C:\PROGRA~1\COMMON~1\Skype\SKYPE4~1.DLL
O20 - AppInit_DLLs: gajapuda.dll
O23 - Service: Adobe LM Service - Adobe Systems - C:\Program Files\Common Files\Adobe Systems Shared\Service\Adobelmsvc.exe
O23 - Service: Apple Mobile Device - Apple Inc. - C:\Program Files\Common Files\Apple\Mobile Device Support\bin\AppleMobileDeviceService.exe
O23 - Service: avast! iAVS4 Control Service (aswUpdSv) - ALWIL Software - C:\Program Files\Alwil Software\Avast4\aswUpdSv.exe
O23 - Service: Ati HotKey Poller - ATI Technologies Inc. - C:\WINDOWS\system32\Ati2evxx.exe
O23 - Service: ATI Smart - Unknown owner - C:\WINDOWS\system32\ati2sgag.exe
O23 - Service: avast! Antivirus - ALWIL Software - C:\Program Files\Alwil Software\Avast4\ashServ.exe
O23 - Service: avast! Mail Scanner - ALWIL Software - C:\Program Files\Alwil Software\Avast4\ashMaiSv.exe
O23 - Service: avast! Web Scanner - ALWIL Software - C:\Program Files\Alwil Software\Avast4\ashWebSv.exe
O23 - Service: Bonjour Service - Apple Inc. - C:\Program Files\Bonjour\mDNSResponder.exe
O23 - Service: FLEXnet Licensing Service - Acresso Software Inc. - C:\Program Files\Common Files\Macrovision Shared\FLEXnet Publisher\FNPLicensingService.exe
O23 - Service: Google Desktop Manager 5.7.806.10245 (GoogleDesktopManager-061008-081103) - Google - C:\Program Files\Google\Google Desktop Search\GoogleDesktop.exe
O23 - Service: InstallDriver Table Manager (IDriverT) - Macrovision Corporation - C:\Program Files\Common Files\InstallShield\Driver\1050\Intel 32\IDriverT.exe
O23 - Service: Imapi Helper - Alex Feinman - C:\Program Files\ISO Recorder\ISO Recorder\ImapiHelper.exe
O23 - Service: iPod Service - Apple Inc. - C:\Program Files\iPod\bin\iPodService.exe
O23 - Service: Java Quick Starter (JavaQuickStarterService) - Sun Microsystems, Inc. - C:\Program Files\Java\jre6\bin\jqs.exe
--
End of file - 8830 bytes
Anything helps, Thanks.
EDIT: This happens on all of my internet browsers.