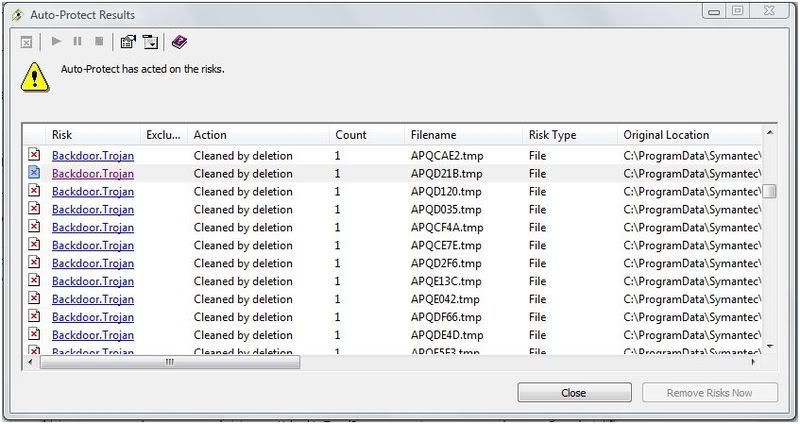
I recently sent in my laptop to HP to replace the battery. When I finally got it back after about 3 months, my antivirus subscription had finished. Now, it seems like I have a trojan or virus on my computer. A program called "Auto-Protect Results" (I think it's part of my antivirus program, I'm not sure) lists that I have MANY "backdoor.trojans" and the program updates every second with more that are found. Here's what it looks like:
[IMG]http://i2.photobucket.com/albums/y49/__sweetcatastrophe/autoprotect.jpg[/IMG]
When I fist started my computer there were only a few, but its since updated to literally thousands of this one 'Backdoor.Trojan" file.
Here's my HijackThis log:
Logfile of Trend Micro HijackThis v2.0.2
Scan saved at 11:47:51, on 2008/7/10
Platform: Windows Vista (WinNT 6.00.1904)
MSIE: Internet Explorer v7.00 (7.00.6000.16681)
Boot mode: Normal
Running processes:
C:\Windows\system32\Dwm.exe
C:\Windows\system32\taskeng.exe
C:\Windows\Explorer.EXE
C:\Program Files\Windows Defender\MSASCui.exe
C:\Program Files\Synaptics\SynTP\SynTPEnh.exe
C:\Program Files\Hewlett-Packard\HP Quick Launch Buttons\QLBCTRL.exe
C:\Program Files\Hewlett-Packard\HP Wireless Assistant\WiFiMsg.exe
C:\Program Files\Hewlett-Packard\HP Wireless Assistant\HPWAMain.exe
C:\Program Files\QuickTime\qttask.exe
C:\Program Files\iTunes\iTunesHelper.exe
C:\Program Files\Common Files\Symantec Shared\ccApp.exe
C:\Windows\System32\rundll32.exe
C:\Program Files\Hewlett-Packard\HP Software Update\hpwuSchd2.exe
C:\Program Files\eFax Messenger 4.3\J2GDllCmd.exe
C:\Program Files\Webroot\Spy Sweeper\SpySweeperUI.exe
C:\Program Files\Windows Sidebar\sidebar.exe
C:\Program Files\Windows Media Player\wmpnscfg.exe
C:\Windows\ehome\ehtray.exe
C:\Program Files\Logitech\Desktop Messenger\8876480\Program\backWeb-8876480.exe
C:\Program Files\eFax Messenger 4.3\J2GTray.exe
C:\Program Files\HP Connections\6811507\Program\HP Connections.exe
C:\Program Files\Hewlett-Packard\Digital Imaging\bin\hpqtra08.exe
C:\Program Files\MIT\Kerberos\bin\netidmgr.exe
C:\Program Files\Microsoft Office\Office12\ONENOTEM.EXE
C:\Windows\ehome\ehmsas.exe
C:\Program Files\MIT\Kerberos\bin\krbcc32s.exe
C:\Windows\System32\bcmwltry.exe
C:\Program Files\Trend Micro\AntiVirus 2007\tavui.exe
C:\PROGRA~1\HEWLET~1\Shared\HPQTOA~1.EXE
C:\Program Files\Hewlett-Packard\Digital Imaging\bin\hpqSTE08.exe
C:\Program Files\Symantec AntiVirus\SavUI.exe
C:\Program Files\Mozilla Firefox\firefox.exe
C:\Windows\system32\wuauclt.exe
C:\Windows\system32\taskeng.exe
C:\Windows\system32\sdclt.exe
C:\Windows\system32\SearchFilterHost.exe
C:\Program Files\Trend Micro\HijackThis\HijackThis.exe
O1 - Hosts: ::1 localhost
O2 - BHO: Adobe PDF Reader Link Helper - {06849E9F-C8D7-4D59-B87D-784B7D6BE0B3} - C:\Program Files\Common Files\Adobe\Acrobat\ActiveX\AcroIEHelper.dll
O2 - BHO: SSVHelper Class - {761497BB-D6F0-462C-B6EB-D4DAF1D92D43} - C:\Program Files\Java\jre1.6.0\bin\ssv.dll
O4 - HKLM\..\Run: [Windows Defender] "C:\Program Files\Windows Defender\MSASCui.exe" -hide
O4 - HKLM\..\Run: [SynTPEnh] "C:\Program Files\Synaptics\SynTP\SynTPEnh.exe"
O4 - HKLM\..\Run: [NvSvc] "RUNDLL32.EXE" C:\Windows\system32\nvsvc.dll,nvsvcStart
O4 - HKLM\..\Run: [NvCplDaemon] "RUNDLL32.EXE" C:\Windows\system32\NvCpl.dll,NvStartup
O4 - HKLM\..\Run: [NvMediaCenter] "RUNDLL32.EXE" C:\Windows\system32\NvMcTray.dll,NvTaskbarInit
O4 - HKLM\..\Run: [QlbCtrl] "C:\Program Files\Hewlett-Packard\HP Quick Launch Buttons\QlbCtrl.exe" /Start
O4 - HKLM\..\Run: [WAWifiMessage] "C:\Program Files\Hewlett-Packard\HP Wireless Assistant\WiFiMsg.exe"
O4 - HKLM\..\Run: [hpWirelessAssistant] "C:\Program Files\Hewlett-Packard\HP Wireless Assistant\HPWAMain.exe"
O4 - HKLM\..\Run: [Trend Micro AntiVirus 2007] "C:\Program Files\Trend Micro\AntiVirus 2007\tavui.exe" -1 --delay 200
O4 - HKLM\..\Run: [QuickTime Task] "C:\Program Files\QuickTime\qttask.exe" -atboottime
O4 - HKLM\..\Run: [iTunesHelper] "C:\Program Files\iTunes\iTunesHelper.exe"
O4 - HKLM\..\Run: [ccApp] "C:\Program Files\Common Files\Symantec Shared\ccApp.exe"
O4 - HKLM\..\Run: [vptray] C:\PROGRA~1\SYMANT~1\VPTray.exe
O4 - HKLM\..\Run: [Adobe Reader Speed Launcher] "C:\Program Files\Adobe\Reader 8.0\Reader\Reader_sl.exe"
O4 - HKLM\..\Run: [HP Software Update] "C:\Program Files\Hewlett-Packard\HP Software Update\HPWuSchd2.exe"
O4 - HKLM\..\Run: [eFax 4.3] "C:\Program Files\eFax Messenger 4.3\J2GDllCmd.exe" /R
O4 - HKLM\..\Run: [SpySweeper] C:\Program Files\Webroot\Spy Sweeper\SpySweeperUI.exe /startintray
O4 - HKCU\..\Run: [Sidebar] "C:\Program Files\Windows Sidebar\sidebar.exe" /autoRun
O4 - HKCU\..\Run: [RunSpySweeperScheduleAtStartup] "C:\Windows\system32\msfeedssync.exe" /ScheduleSweep=User_Feed_Synchronization-{1949C9A1-796B-497A-835E-E5CE0B303A6A}
O4 - HKCU\..\Run: [WMPNSCFG] "C:\Program Files\Windows Media Player\WMPNSCFG.exe"
O4 - HKCU\..\Run: [ehTray.exe] C:\Windows\ehome\ehTray.exe
O4 - HKCU\..\Run: [ISUSPM Startup] "C:\PROGRA~1\COMMON~1\INSTAL~1\UPDATE~1\ISUSPM.exe" -startup
O4 - HKCU\..\Run: [LDM] "C:\Program Files\Logitech\Desktop Messenger\8876480\Program\BackWeb-8876480.exe"
O4 - HKUS\S-1-5-19\..\Run: [Sidebar] %ProgramFiles%\Windows Sidebar\Sidebar.exe /detectMem (User 'LOCAL SERVICE')
O4 - HKUS\S-1-5-19\..\Run: [WindowsWelcomeCenter] rundll32.exe oobefldr.dll,ShowWelcomeCenter (User 'LOCAL SERVICE')
O4 - HKUS\S-1-5-20\..\Run: [Sidebar] %ProgramFiles%\Windows Sidebar\Sidebar.exe /detectMem (User 'NETWORK SERVICE')
O4 - Startup: OneNote 2007 Screen Clipper and Launcher.lnk = C:\Program Files\Microsoft Office\Office12\ONENOTEM.EXE
O4 - Global Startup: Adobe Gamma Loader.lnk = C:\Program Files\Common Files\Adobe\Calibration\Adobe Gamma Loader.exe
O4 - Global Startup: eFax 4.3.lnk = C:\Program Files\eFax Messenger 4.3\J2GTray.exe
O4 - Global Startup: HP Connections.lnk = C:\Program Files\HP Connections\6811507\Program\HP Connections.exe
O4 - Global Startup: HP Digital Imaging Monitor.lnk = C:\Program Files\Hewlett-Packard\Digital Imaging\bin\hpqtra08.exe
O4 - Global Startup: Logitech Desktop Messenger.lnk = C:\Program Files\Logitech\Desktop Messenger\8876480\Program\LDMConf.exe
O4 - Global Startup: MRI_DISABLED
O4 - Global Startup: Network Identity Manager.lnk = C:\Program Files\MIT\Kerberos\bin\netidmgr.exe
O8 - Extra context menu item: E&xport to Microsoft Excel - res://C:\PROGRA~1\MICROS~3\Office12\EXCEL.EXE/3000
O9 - Extra button: (no name) - {08B0E5C0-4FCB-11CF-AAA5-00401C608501} - C:\Program Files\Java\jre1.6.0\bin\ssv.dll
O9 - Extra 'Tools' menuitem: Sun Java Console - {08B0E5C0-4FCB-11CF-AAA5-00401C608501} - C:\Program Files\Java\jre1.6.0\bin\ssv.dll
O9 - Extra button: Send to OneNote - {2670000A-7350-4f3c-8081-5663EE0C6C49} - C:\PROGRA~1\MICROS~3\Office12\ONBttnIE.dll
O9 - Extra 'Tools' menuitem: S&end to OneNote - {2670000A-7350-4f3c-8081-5663EE0C6C49} - C:\PROGRA~1\MICROS~3\Office12\ONBttnIE.dll
O9 - Extra button: Research - {92780B25-18CC-41C8-B9BE-3C9C571A8263} - C:\PROGRA~1\MICROS~3\Office12\REFIEBAR.DLL
O10 - Unknown file in Winsock LSP: c:\windows\system32\tmlsp.dll
O10 - Unknown file in Winsock LSP: c:\windows\system32\tmlsp.dll
O10 - Unknown file in Winsock LSP: c:\windows\system32\tmlsp.dll
O10 - Unknown file in Winsock LSP: c:\windows\system32\tmlsp.dll
O10 - Unknown file in Winsock LSP: c:\windows\system32\tmlsp.dll
O10 - Unknown file in Winsock LSP: c:\windows\system32\tmlsp.dll
O10 - Unknown file in Winsock LSP: c:\windows\system32\tmlsp.dll
O13 - Gopher Prefix:
O15 - ESC Trusted Zone:
O16 - DPF: {165D83D3-359C-4783-9BF0-6FA6DC42A3F1} -
O16 - DPF: {1DE88635-1C72-401E-B23B-93FA86D30F3B} -
O16 - DPF: {6F15128C-E66A-490C-B848-5000B5ABEEAC} (HP Download Manager) -
O16 - DPF: {CF40ACC5-E1BB-4AFF-AC72-04C2F616BCA7} (get_atlcom Class) -
O16 - DPF: {FFBB3F3B-0A5A-4106-BE53-DFE1E2340CB1} (DownloadManager Control) -
O17 - HKLM\System\CCS\Services\Tcpip\Parameters: Domain = stanford.edu
O17 - HKLM\Software\..\Telephony: DomainName = stanford.edu
O17 - HKLM\System\CS1\Services\Tcpip\Parameters: Domain = stanford.edu
O17 - HKLM\System\CS2\Services\Tcpip\Parameters: Domain = stanford.edu
O20 - Winlogon Notify: MIT_KFW - C:\Windows\system32\kfwlogon.dll
O23 - Service: AddFiltr - Hewlett-Packard Development Company, L.P. - C:\Program Files\Hewlett-Packard\HP Quick Launch Buttons\AddFiltr.exe
O23 - Service: Apple Mobile Device - Apple, Inc. - C:\Program Files\Common Files\Apple\Mobile Device Support\bin\AppleMobileDeviceService.exe
O23 - Service: Symantec Event Manager (ccEvtMgr) - Symantec Corporation - C:\Program Files\Common Files\Symantec Shared\ccSvcHst.exe
O23 - Service: Symantec Settings Manager (ccSetMgr) - Symantec Corporation - C:\Program Files\Common Files\Symantec Shared\ccSvcHst.exe
O23 - Service: CyberLink Background Capture Service (CBCS) (CLCapSvc) - Unknown owner - C:\Program Files\HP\QuickPlay\Kernel\TV\CLCapSvc.exe
O23 - Service: CyberLink Task Scheduler (CTS) (CLSched) - Unknown owner - C:\Program Files\HP\QuickPlay\Kernel\TV\CLSched.exe
O23 - Service: Symantec Lic NetConnect service (CLTNetCnService) - Symantec Corporation - c:\Program Files\Common Files\Symantec Shared\ccSvcHst.exe
O23 - Service: Symantec AntiVirus Definition Watcher (DefWatch) - Symantec Corporation - C:\Program Files\Symantec AntiVirus\DefWatch.exe
O23 - Service: Google Updater Service (gusvc) - Google - C:\Program Files\Google\Common\Google Updater\GoogleUpdaterService.exe
O23 - Service: HP Health Check Service - Hewlett-Packard - C:\Program Files\Hewlett-Packard\HP Health Check\hphc_service.exe
O23 - Service: hpqwmiex - Hewlett-Packard Development Company, L.P. - C:\Program Files\Hewlett-Packard\Shared\hpqwmiex.exe
O23 - Service: InstallDriver Table Manager (IDriverT) - Macrovision Corporation - C:\Program Files\Roxio\Roxio MyDVD Basic v9\InstallShield\Driver\1050\Intel 32\IDriverT.exe
O23 - Service: iPod 服务 (iPod Service) - Apple Inc. - C:\Program Files\iPod\bin\iPodService.exe
O23 - Service: LightScribeService Direct Disc Labeling Service (LightScribeService) - Hewlett-Packard Company - C:\Program Files\Common Files\LightScribe\LSSrvc.exe
O23 - Service: LiveUpdate - Symantec Corporation - C:\PROGRA~1\Symantec\LIVEUP~1\LUCOMS~1.EXE
O23 - Service: RoxMediaDB9 - Sonic Solutions - C:\Program Files\Common Files\Roxio Shared\9.0\SharedCOM\RoxMediaDB9.exe
O23 - Service: SAVRoam (SavRoam) - symantec - C:\Program Files\Symantec AntiVirus\SavRoam.exe
O23 - Service: stllssvr - MicroVision Development, Inc. - C:\Program Files\Common Files\SureThing Shared\stllssvr.exe
O23 - Service: Symantec AntiVirus - Symantec Corporation - C:\Program Files\Symantec AntiVirus\Rtvscan.exe
O23 - Service: Trend Micro AntiVirus Protection Service (tavsvc) - Trend Micro Inc. - C:\Program Files\Trend Micro\AntiVirus 2007\tavsvc.exe
O23 - Service: Trend Micro Proxy Service (tmproxy) - Trend Micro Inc. - C:\Program Files\Trend Micro\AntiVirus 2007\Components\tmproxy.exe
O23 - Service: wampapache - Apache Software Foundation - c:\wamp\apache2\bin\httpd.exe
O23 - Service: wampmysqld - Unknown owner - c:\wamp\mysql\bin\mysqld-nt.exe
O23 - Service: Webroot Spy Sweeper Engine (WebrootSpySweeperService) - Webroot Software, Inc. - C:\Program Files\Webroot\Spy Sweeper\SpySweeper.exe
O23 - Service: WLTRYSVC - Unknown owner - C:\Windows\System32\wltrysvc.exe
O23 - Service: XAudioService - Conexant Systems, Inc. - C:\Windows\system32\DRIVERS\xaudio.exe
--
End of file - 11147 bytesIf anyone could help me get rid of this trojan it would be greatly appreciated. Thanks!!