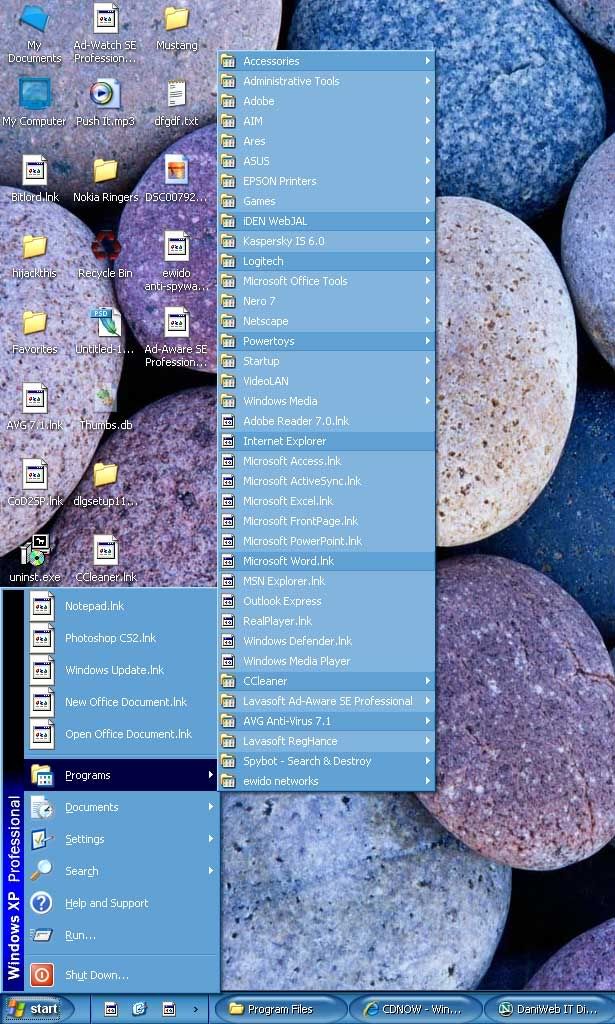
My shortcuts have stopped working since this morning when my PC did its normal auto shutoff after completing 5 torrent downloads which were just 4 .avi videos and one adaware 1.06r1 since I started up my this morning none of my normal RUN items started up by themselves and all of my quick start/programs icons are not working. Also all of my .exe files were not working by I fixed that issue with this fix:
"If you're unable to launch Regedit.exe even from Command Prompt, try this:
copy regedit.exe regedit.com
regedit.com" I ran it thorugh cmd prompt with alt+ctrl+del while holding ctrl key and choosing run new task."
Now my last issue is no shortcuts even creating a new one, I just get a blank useless .INK file or LNK file cannot be opened, and when I logon at start up a blank window opens before the logon window, here is what it looks like now along with my hijackthis logs and ewido report:
[img]http://i36.photobucket.com/albums/e25/risho85/shortcuts.jpg[/img]
Logfile of HijackThis v1.99.1
Scan saved at 6:08:49 PM, on 8/24/2006
Platform: Windows XP SP2 (WinNT 5.01.2600)
MSIE: Internet Explorer v7.00 (7.00.5450.0004)
Running processes:
F:\WINDOWS\System32\smss.exe
F:\WINDOWS\system32\winlogon.exe
F:\WINDOWS\system32\services.exe
F:\WINDOWS\system32\lsass.exe
F:\WINDOWS\system32\svchost.exe
F:\Program Files\Windows Defender\MsMpEng.exe
F:\WINDOWS\System32\svchost.exe
F:\Program Files\TGTSoft\StyleXP\StyleXPService.exe
F:\WINDOWS\system32\spoolsv.exe
F:\Program Files\Common Files\EPSON\EBAPI\eEBSVC.exe
F:\PROGRA~1\Grisoft\AVG7\avgamsvr.exe
F:\PROGRA~1\Grisoft\AVG7\avgupsvc.exe
F:\PROGRA~1\Grisoft\AVG7\avgemc.exe
F:\Program Files\Common Files\EPSON\EBAPI\SAgent2.exe
F:\WINDOWS\system32\nvsvc32.exe
F:\WINDOWS\system32\svchost.exe
F:\WINDOWS\Explorer.EXE
F:\PROGRA~1\Grisoft\AVG7\avgcc.exe
F:\WINDOWS\system32\ctfmon.exe
F:\Program Files\Spybot - Search & Destroy\TeaTimer.exe
F:\Program Files\Internet Explorer\iexplore.exe
F:\Program Files\uTorrent\utorrent.exe
F:\Program Files\Ares\Ares.exe
F:\Program Files\Netscape\Netscape Browser\netscape.exe
F:\Program Files\ewido anti-spyware 4.0\guard.exe
F:\Program Files\ewido anti-spyware 4.0\ewido.exe
F:\Program Files\Adobe\Adobe Photoshop CS2\Photoshop.exe
F:\DOCUME~1\En\LOCALS~1\Temp\Adobelm_Cleanup.0001
F:\Program Files\Common Files\Adobe Systems Shared\Service\Adobelmsvc.exe
F:\DOCUME~1\En\LOCALS~1\Temp\Adobelm_Cleanup.0001
F:\WINDOWS\system32\NOTEPAD.EXE
F:\Documents and Settings\En\Desktop\hijackthis\HijackThis.exe
R0 - HKCU\Software\Microsoft\Internet Explorer\Main,Start Page = http://www.yahoo.com/
R0 - HKLM\Software\Microsoft\Internet Explorer\Main,Start Page =
R0 - HKLM\Software\Microsoft\Internet Explorer\Search,SearchAssistant =
R0 - HKLM\Software\Microsoft\Internet Explorer\Search,CustomizeSearch =
R0 - HKCU\Software\Microsoft\Internet Explorer\Main,Local Page =
R0 - HKLM\Software\Microsoft\Internet Explorer\Main,Local Page =
O1 - Hosts:
O2 - BHO: AcroIEHlprObj Class - {06849E9F-C8D7-4D59-B87D-784B7D6BE0B3} - F:\Program Files\Adobe\Acrobat 7.0\ActiveX\AcroIEHelper.dll
O2 - BHO: SSVHelper Class - {761497BB-D6F0-462C-B6EB-D4DAF1D92D43} - F:\Program Files\Java\jre1.5.0_06\bin\ssv.dll
O2 - BHO: Trixie.Bho - {B0744341-96E0-4341-9ED2-8BC36CE0CCD0} - mscoree.dll (file missing)
O2 - BHO: CoTGT_BHO Class - {C333CF63-767F-4831-94AC-E683D962C63C} - F:\Program Files\TGTSoft\StyleXP\TGT_BHO.dll
O4 - HKLM\..\Run: [KernelFaultCheck] %systemroot%\system32\dumprep 0 -k
O4 - HKLM\..\Run: [NvCplDaemon] RUNDLL32.EXE F:\WINDOWS\system32\NvCpl.dll,NvStartup
O4 - HKLM\..\Run: [AVG7_CC] F:\PROGRA~1\Grisoft\AVG7\avgcc.exe /STARTUP
O4 - HKCU\..\Run: [ctfmon.exe] F:\WINDOWS\system32\ctfmon.exe
O4 - HKCU\..\Run: [SpybotSD TeaTimer] F:\Program Files\Spybot - Search & Destroy\TeaTimer.exe
O4 - Global Startup: Logitech SetPoint.lnk = F:\Program Files\Logitech\SetPoint\SetPoint.exe
O8 - Extra context menu item: &ieSpell Options - res://F:\Program Files\ieSpell\iespell.dll/SPELLOPTION.HTM
O8 - Extra context menu item: Check &Spelling - res://F:\Program Files\ieSpell\iespell.dll/SPELLCHECK.HTM
O8 - Extra context menu item: E&xport to Microsoft Excel - res://F:\PROGRA~1\MICROS~2\Office10\EXCEL.EXE/3000
O9 - Extra button: (no name) - {08B0E5C0-4FCB-11CF-AAA5-00401C608501} - F:\Program Files\Java\jre1.5.0_06\bin\ssv.dll
O9 - Extra 'Tools' menuitem: Sun Java Console - {08B0E5C0-4FCB-11CF-AAA5-00401C608501} - F:\Program Files\Java\jre1.5.0_06\bin\ssv.dll
O9 - Extra button: ieSpell - {0E17D5B7-9F5D-4fee-9DF6-CA6EE38B68A8} - F:\Program Files\ieSpell\iespell.dll
O9 - Extra 'Tools' menuitem: ieSpell - {0E17D5B7-9F5D-4fee-9DF6-CA6EE38B68A8} - F:\Program Files\ieSpell\iespell.dll
O9 - Extra button: (no name) - {1606D6F9-9D3B-4aea-A025-ED5B2FD488E7} - F:\Program Files\ieSpell\iespell.dll
O9 - Extra 'Tools' menuitem: ieSpell Options - {1606D6F9-9D3B-4aea-A025-ED5B2FD488E7} - F:\Program Files\ieSpell\iespell.dll
O9 - Extra button: (no name) - {20CCCFEC-D26F-4ffe-996B-388B39C8CCCA} - F:\WINDOWS\system32\mscoree.DLL
O9 - Extra 'Tools' menuitem: Tri&xie Options... - {20CCCFEC-D26F-4ffe-996B-388B39C8CCCA} - F:\WINDOWS\system32\mscoree.DLL
O9 - Extra button: Create Mobile Favorite - {2EAF5BB1-070F-11D3-9307-00C04FAE2D4F} - F:\PROGRA~1\MICROS~3\INetRepl.dll
O9 - Extra button: (no name) - {2EAF5BB2-070F-11D3-9307-00C04FAE2D4F} - F:\PROGRA~1\MICROS~3\INetRepl.dll
O9 - Extra 'Tools' menuitem: Create Mobile Favorite... - {2EAF5BB2-070F-11D3-9307-00C04FAE2D4F} - F:\PROGRA~1\MICROS~3\INetRepl.dll
O9 - Extra button: Messenger - {FB5F1910-F110-11d2-BB9E-00C04F795683} - F:\Program Files\Messenger\msmsgs.exe
O9 - Extra 'Tools' menuitem: Windows Messenger - {FB5F1910-F110-11d2-BB9E-00C04F795683} - F:\Program Files\Messenger\msmsgs.exe
O16 - DPF: {6414512B-B978-451D-A0D8-FCFDF33E833C} (WUWebControl Class) -
O23 - Service: Adobe LM Service - Adobe Systems - F:\Program Files\Common Files\Adobe Systems Shared\Service\Adobelmsvc.exe
O23 - Service: AVG7 Alert Manager Server (Avg7Alrt) - GRISOFT, s.r.o. - F:\PROGRA~1\Grisoft\AVG7\avgamsvr.exe
O23 - Service: AVG7 Update Service (Avg7UpdSvc) - GRISOFT, s.r.o. - F:\PROGRA~1\Grisoft\AVG7\avgupsvc.exe
O23 - Service: AVG E-mail Scanner (AVGEMS) - GRISOFT, s.r.o. - F:\PROGRA~1\Grisoft\AVG7\avgemc.exe
O23 - Service: EpsonBidirectionalService - Unknown owner - F:\Program Files\Common Files\EPSON\EBAPI\eEBSVC.exe
O23 - Service: EPSON Printer Status Agent2 (EPSONStatusAgent2) - SEIKO EPSON CORPORATION - F:\Program Files\Common Files\EPSON\EBAPI\SAgent2.exe
O23 - Service: ewido anti-spyware 4.0 guard - Anti-Malware Development a.s. - F:\Program Files\ewido anti-spyware 4.0\guard.exe
O23 - Service: InstallDriver Table Manager (IDriverT) - Macrovision Corporation - F:\Program Files\Common Files\InstallShield\Driver\11\Intel 32\IDriverT.exe
O23 - Service: NVIDIA Display Driver Service (NVSvc) - NVIDIA Corporation - F:\WINDOWS\system32\nvsvc32.exe
O23 - Service: StarWind iSCSI Service (StarWindService) - Unknown owner - F:\Program Files\Alcohol Soft\Alcohol 120\StarWind\StarWindService.exe (file missing)
O23 - Service: StyleXPService - Unknown owner - F:\Program Files\TGTSoft\StyleXP\StyleXPService.exe
My Ewideo Report after a scan in my desktop w/o safe mode
---------------------------------------------------------
ewido anti-spyware - Scan Report
---------------------------------------------------------
+ Created at: 6:09:27 PM 8/24/2006
+ Scan result:
D:\My Documents\Other\Get To\hijackthis\backups\backup-20051205-150459-281.dll -> Adware.Minibug : Cleaned.
D:\My Documents\Games\Main Files\Dope Wars\dopewarsv1.23trainer\Trainer.exe -> Dropper.Small : Cleaned.
D:\My Documents\Other\PC - Info - Etc\Back-Ups\Key Generators - Hacks - Serials\PCBoost v3.2.21.2005\PcBoost.exe -> Logger.Banker : Cleaned.
:mozilla.10:F:\Documents and Settings\LocalService\Application Data\Netscape\NSB\Profiles\h87udxn6.default\cookies.txt -> TrackingCookie.2o7 : Cleaned.
:mozilla.11:F:\Documents and Settings\LocalService\Application Data\Netscape\NSB\Profiles\h87udxn6.default\cookies.txt -> TrackingCookie.2o7 : Cleaned.
:mozilla.46:F:\Documents and Settings\En\Application Data\Netscape\NSB\Profiles\wjtbgi27.default\cookies.txt -> TrackingCookie.Addynamix : Cleaned.
F:\Documents and Settings\En\Cookies\dynamix[1].txt -> TrackingCookie.Addynamix : Cleaned.
:mozilla.33:F:\Documents and Settings\En\Application Data\Netscape\NSB\Profiles\wjtbgi27.default\cookies.txt -> TrackingCookie.Adjuggler : Cleaned.
:mozilla.34:F:\Documents and Settings\En\Application Data\Netscape\NSB\Profiles\wjtbgi27.default\cookies.txt -> TrackingCookie.Adjuggler : Cleaned.
:mozilla.35:F:\Documents and Settings\En\Application Data\Netscape\NSB\Profiles\wjtbgi27.default\cookies.txt -> TrackingCookie.Adjuggler : Cleaned.
:mozilla.36:F:\Documents and Settings\En\Application Data\Netscape\NSB\Profiles\wjtbgi27.default\cookies.txt -> TrackingCookie.Adjuggler : Cleaned.
F:\Documents and Settings\En\Cookies\juggler[2].txt -> TrackingCookie.Adjuggler : Cleaned.
:mozilla.26:F:\Documents and Settings\En\Application Data\Netscape\NSB\Profiles\wjtbgi27.default\cookies.txt -> TrackingCookie.Advertising : Cleaned.
:mozilla.27:F:\Documents and Settings\En\Application Data\Netscape\NSB\Profiles\wjtbgi27.default\cookies.txt -> TrackingCookie.Advertising : Cleaned.
:mozilla.28:F:\Documents and Settings\En\Application Data\Netscape\NSB\Profiles\wjtbgi27.default\cookies.txt -> TrackingCookie.Advertising : Cleaned.
:mozilla.29:F:\Documents and Settings\En\Application Data\Netscape\NSB\Profiles\wjtbgi27.default\cookies.txt -> TrackingCookie.Advertising : Cleaned.
F:\Documents and Settings\En\Cookies\en@advertising[1].txt -> TrackingCookie.Advertising : Cleaned.
:mozilla.25:F:\Documents and Settings\En\Application Data\Netscape\NSB\Profiles\wjtbgi27.default\cookies.txt -> TrackingCookie.Atdmt : Cleaned.
F:\Documents and Settings\En\Cookies\en@atdmt[1].txt -> TrackingCookie.Atdmt : Cleaned.
:mozilla.30:F:\Documents and Settings\En\Application Data\Netscape\NSB\Profiles\wjtbgi27.default\cookies.txt -> TrackingCookie.Doubleclick : Cleaned.
F:\Documents and Settings\En\Cookies\en@doubleclick[2].txt -> TrackingCookie.Doubleclick : Cleaned.
:mozilla.18:F:\Documents and Settings\En\Application Data\Netscape\NSB\Profiles\wjtbgi27.default\cookies.txt -> TrackingCookie.Fastclick : Cleaned.
:mozilla.19:F:\Documents and Settings\En\Application Data\Netscape\NSB\Profiles\wjtbgi27.default\cookies.txt -> TrackingCookie.Fastclick : Cleaned.
:mozilla.21:F:\Documents and Settings\En\Application Data\Netscape\NSB\Profiles\wjtbgi27.default\cookies.txt -> TrackingCookie.Fastclick : Cleaned.
F:\Documents and Settings\En\Cookies\en@fastclick[2].txt -> TrackingCookie.Fastclick : Cleaned.
:mozilla.22:F:\Documents and Settings\En\Application Data\Netscape\NSB\Profiles\wjtbgi27.default\cookies.txt -> TrackingCookie.Tribalfusion : Cleaned.
:mozilla.23:F:\Documents and Settings\En\Application Data\Netscape\NSB\Profiles\wjtbgi27.default\cookies.txt -> TrackingCookie.Tribalfusion : Cleaned.
:mozilla.24:F:\Documents and Settings\En\Application Data\Netscape\NSB\Profiles\wjtbgi27.default\cookies.txt -> TrackingCookie.Tribalfusion : Cleaned.
F:\Documents and Settings\En\Cookies\en@tribalfusion[2].txt -> TrackingCookie.Tribalfusion : Cleaned.
::Report end