YouTube fixes Justin Bieber porn hack hole

happygeek 1 Tallied Votes 876 Views Share

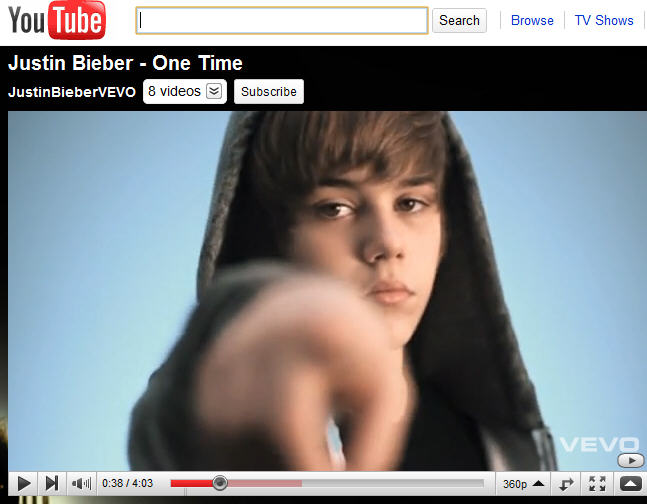
Hackers have targeted Justin Bieber videos on YouTube, exploiting a cross-site scripting vulnerability which enabled them to bombard viewers with pop-up messages and redirect them to porn sites. The hack attack lasted for the best part of two hours before Google was able to isolate the problem and apply a fix.

As well as using Justin Bieber video clips as the bait for the attack, the hackers also took the opportunity to leave abusive and obscene comments about the popular teen idol singer. A number of banner messages even appeared beneath the most popular Bieber videos proclaiming that he was dead. A Google spokesman told The Telegraph that the YouTube hack had been dealt with swiftly , claiming "Comments were temporarily hidden by default within an hour, and we released a complete fix for the issue in about two hours. We’re continuing to study the vulnerability to help prevent similar issues in the future."

Meanwhile, security expert Graham Cluley points out that this is a big target with millions of visitors a day and hopes that , as well as "explore if they are reviewing code properly before it is made live to ensure that loopholes aren't left in their code in future."

This isn't the first time that Justin Bieber has found himself at the centre of an online controversy. DaniWeb has previously reported how Twitter tweaked its trending algorithm to prevent Justin Bieber being at the top all the time, and a service which took delight in removing all traces of Bieber also courted controversy.
Dani AI

Generated

As outlined, this thread describes a classic cross‑site scripting (XSS) event on high‑traffic user content. That mix — large audience plus user‑supplied comments/descriptions — makes any XSS especially damaging. ’s concern about younger viewers is valid: aside from offensive content, injected scripts can deliver redirects, fake login prompts, or drive‑by attacks. is right that fast mitigation matters, but short fixes must be followed by deeper hardening.

Quick primer: XSS happens when untrusted input is included in a page without context‑aware encoding. Stored XSS (comments/descriptions), reflected XSS (crafted URLs) and DOM XSS (client‑side DOM writes) all let attackers run JavaScript in other users’ browsers, which can open popups, change window.location, insert forms, or manipulate the page DOM.

Practical mitigations for site operators:

  • Treat every piece of user content as untrusted; apply context‑aware output encoding (HTML body, HTML attribute, JavaScript string, URL).

  • Use templating frameworks that auto‑escape by default and avoid rendering raw HTML from users.

  • If allowing limited markup, sanitize with a whitelist sanitizer on the server side and recheck on the client.

  • Add a Content Security Policy (CSP) to limit where scripts can come from. Example header:

    Content-Security-Policy: default-src 'self'; script-src 'self' 'nonce-<RANDOM_NONCE>'; object-src 'none'; base-uri 'self'; frame-ancestors 'none';
  • Enforce HttpOnly/Secure cookies, keep libraries patched, run automated SAST/DAST scans and periodic pen tests, and prepare an incident response playbook.

Advice for readers/viewers: keep browsers updated, avoid clicking suspicious comment links, report offending content, consider a script blocker for untrusted pages, and if you visited a site that requested credentials, change passwords and review account activity.

Layered controls (encoding + sanitization + CSP + monitoring + quick takedown) are what stop repeats — removing visible payloads helps immediately, but fixing the rendering pipeline prevents the next attack.

vivifoster 0 Light Poster

beiber is so popular that hackers decided to use him. unfortunately, what good would it give them? bieber's audience are kids?? are they trying to be more disgusting than usual?

Member 784494 0 Newbie Poster

There are a lot of greedy sick people out there, just be aware and pass on the details to someone that can fix this... glad google was on top of the situation. Braven.

tz2010 -1 Newbie Poster

Thanks for the info, I appreciate it.

joelchrist -9 Posting Whiz

Its really a great news, Thanks for sharing.

dnanetwork 18 Practically a Master Poster Banned

this is really cool stuff..

Be a part of the DaniWeb community

We're a friendly, industry-focused community of developers, IT pros, digital marketers, and technology enthusiasts meeting, networking, learning, and sharing knowledge.