Oh the irony. In what is starting to read very much like the script to a Hollywood movie itself, the latest twist to the Sony Pictures hacking plot took an unexpected turn yesterday. It would appear that at one stage yesterday access to the web across pretty much all of North Korea went down, with access to key sites such as the state-run Korean Central News Agency (KCNA) and Rodong Sinmun newspaper were down for most of the day. Not that most North Koreans would have noticed, of course, seeing as they are denied access to the Internet anyway.
The question now is who did it, assuming anyone did that is as a technical glitch is not entirely out of the question although highly unlikely truth be told. News sources online immediately seized upon the US as being the prime suspect, given that the FBI had officially blamed North Korea on December 19th for being behind the Sony Pictures attack. Retaliation of some sort was not a total surprise, with President Obama promising a 'proportional response' however a cyber-attack on the scale required to take down country-wide nation state access would be quite some undertaking. The finger pointing is prompted by reports that security outfits which monitor such things, such as Arbor Networks, had noticed that the Internet infrastructure in North Korea started to suffer from denial-of-service attacks from December 20th; the day after the FBI announcement. However, dig a little deeper and you will discover that Arbor actually noted these attacks starting the day before the FBI statement on the 18th. This anomaly, some are saying, suggests that it was not part of the US proportionate response that Obama spoke of.
I tend to agree that it is unlikely to have been a state-sponsored attack, especially coming out of the US. Not least because the evidence, such that it is at this time, suggests that the denial-of-service attacks were relatively small scale and took a number of days to reach a climactic collapse point. Surely if the US were behind this, and if it were done in order to make a statement to the North Korean regime, that collapse would have been immediate and catastrophic rather than gradual and patchy? There is no doubting that US forces have the capability to perform such an attack, and perform it with some vigour. Then there is the China implication. If the US was, indeed, behind the outages then it would be a very bold move. Not just because North Korea is, to say the least, something of an unstable and unpredictable actor; but also because the North Korean internet is routed via Star Joint Ventures through the Chinese provider China Unicom. China has long supported North Korea politically, and to attack the regime could be seen as attacking China itself given the technicalities involved in such a denial-of-service bombing.
So if not the US, then who? It would be relatively easy to blame South Korea as there is no love lost between the two neighbours (he says attempting to win the understatement of the year award) and it has just suffered a breach aimed at the country's nuclear power plants. However, just as with the Sony Pictures breach, there is no actual evidence that North Korea was behind this. All there is, is suspicion and that is unlikely to be enough to prompt an act of cyberwar. Which leaves us where? Well the Lizard Unit https://twitter.com/lizardunit has already claimed responsibility. The who now? DaniWeb reported on this group of hackers a couple of weeks ago when it claimed to have taken down the Microsoft Xbox Live network and threatened more attacks to come.
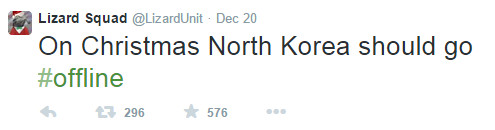
On December 20th the group posted a message stating "On Christmas North Korea should go #offline" and then followed this up yesterday with "North Korea #offline" and "Xbox Live & other targets have way more capacity. North Korea is a piece of cake." None of which is to say the group were actually responsible, but it's at least as likely that such an outfit were behind the denial-of-service, if not more so, than a nation state.